The ITSPmagazine Podcast
Founded in 2015, ITSPmagazine began as a vision for a publication positioned at the critical intersection of technology, cybersecurity, and society. What started as a written publication has evolved into a comprehensive repository for all their content—podcasts, articles, event coverage, interviews, videos, panels, and everything they create. This is where Sean Martin and Marco Ciappelli talk about cybersecurity, technology, society, music, storytelling, branding, conference coverage, and whatever else catches their attention. Over a decade of conversations exploring how these worlds collide, influence each other, and shape the human experience. This is where you'll find it all.
Phishing Training Looks the Same Under Three Mindsets | Human-Centered Cybersecurity Series with Co-Host Julie Haney and Guest Verena Zimmermann | Redefining CyberSecurity with Sean Martin
Show notes
Phishing training looks like one measure from the outside. Verena Zimmermann, Assistant Professor (Tenure Track) for Security, Privacy and Society at ETH Zürich, says it can be classified as a constraining, considering or enabling approach, and that "the intervention itself doesn't necessarily tell us a lot about the mindset that's behind it, and I think that's, that's crucial because that's the starting point." Zimmermann joins Sean Martin and co-host Julie Haney to discuss the article she co-authored, "Human-Centered Cybersecurity Revisited: From Enemies to Partners."
Zimmermann uses phishing to make the mindsets concrete. A...
No Brand Is a Brand — What a Store in Ginza Taught Me About Something I Wrote in 1996
Ginza on a weekday afternoon. Chanel. Dior. Louis Vuitton. Gucci. Cartier. Bulgari. Glass, gold, polished stone. If there's a street on this planet that has turned the logo into architecture, this is it.
And right there, among them, a big store with its name across the front. Muji. Short for Mujirushi Ryohin. No brand, quality goods.
I laughed. Out loud, on the sidewalk, like a tourist who just got the joke. Because I had written that joke, more or less, in 1996.
My master's thesis at the University of Florence was on advertising and...
Halloween and the Little Robots
Halloween and the Little Robots
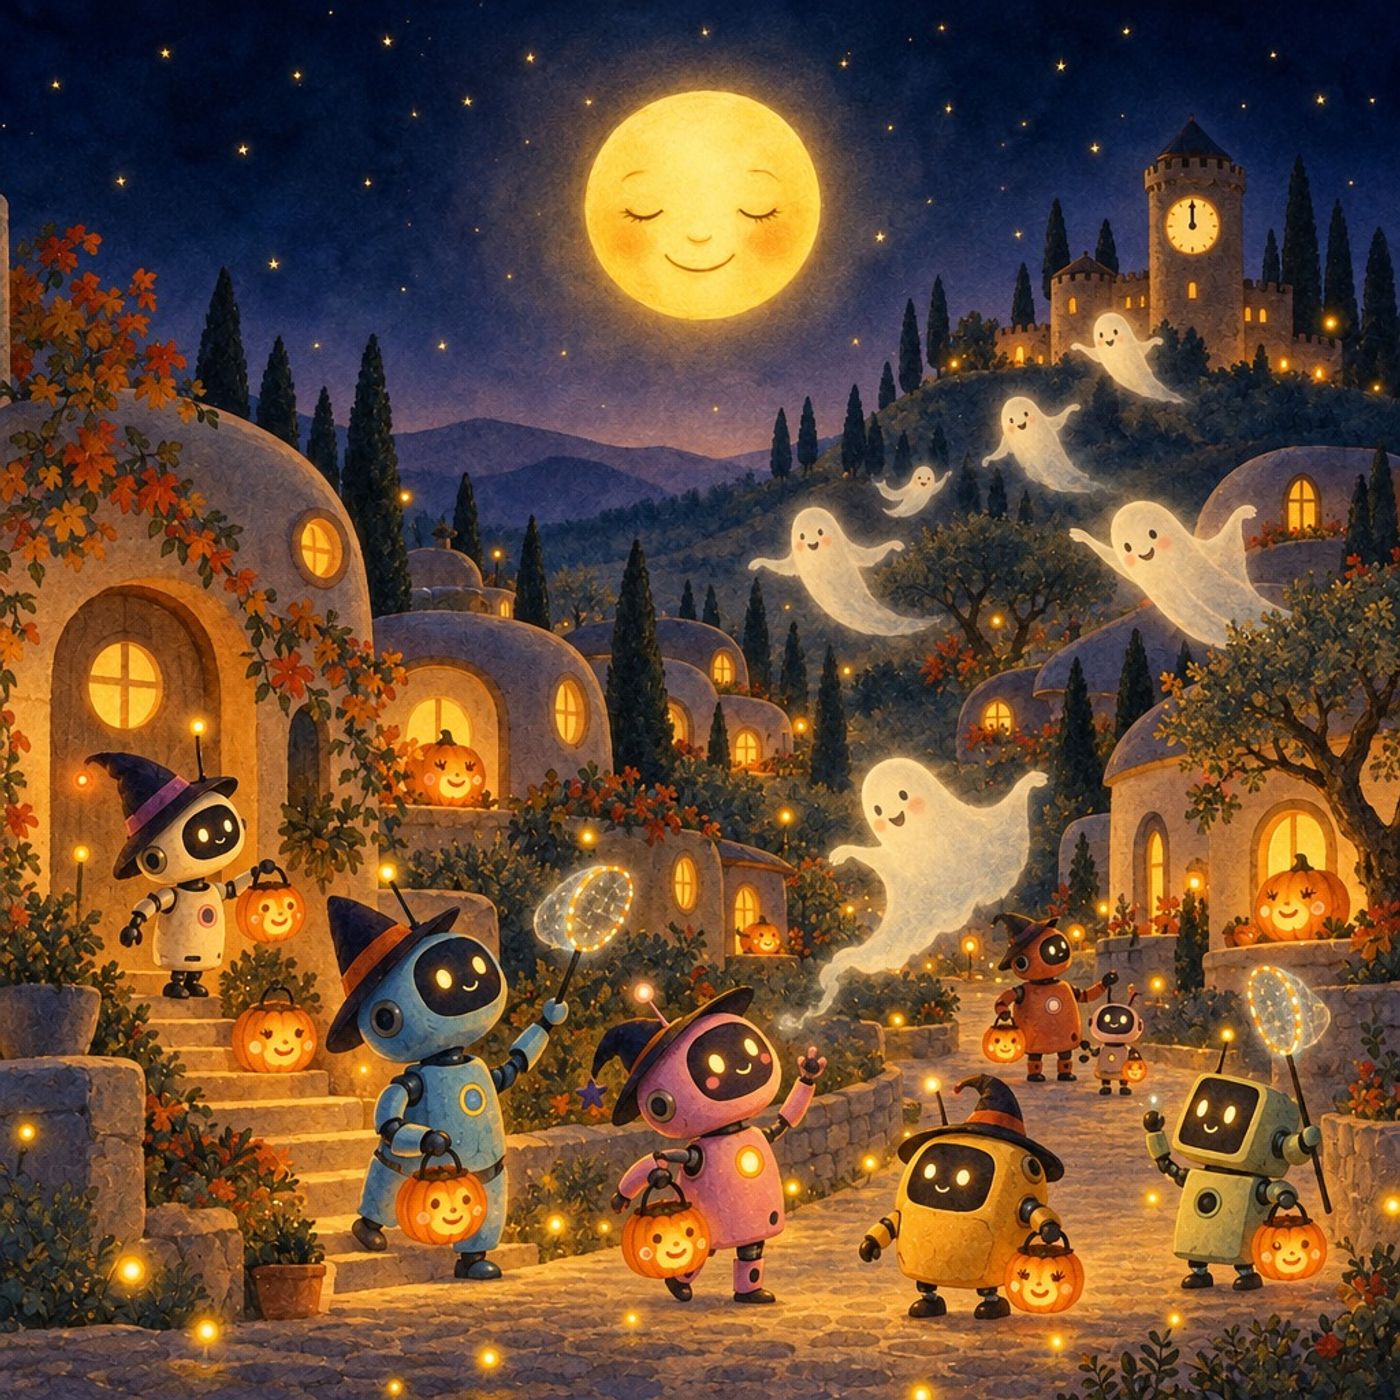
In the world of tomorrow there is a village of the future, whose inhabitants are little robots.
“It’s Halloween — let’s get ready to celebrate!” shouted the robots of the village of the future, all together.
The pumpkins woke at dawn, washed their faces with the dew and, humming, put on their make-up.
They took their places on the windowsills and in front of the doors of the houses, each with its own candle.
With witches’ hats on their heads and baskets shaped like glowing...
Using AI to Cut GRC Busywork Without Cutting Out the Human | A Redefining CyberSecurity Podcast Conversation with Princess Okoro, Manager, Security Governance, Risk and Compliance of Trainline
Guardrails matter as much as the prompt. Princess Okoro tells the agent what it must not do, anchors it to named standards such as ISO and PCI DSS, and instructs it to come back with questions when it is unsure instead of hallucinating. The same thinking shows up in Ask Infosec, an internal custom GPT that answers policy questions for the business, and in a growing map from policy to control to risk that feeds a unified control framework at Trainline.
Tooling comes with trade-offs. Trainline is implementing a GRC platform chosen because it handles risk better...
Nobody Says Good Morning to a Shovel. Should You Say It to Your AI? | A Random and Unscripted Conversation with Sean Martin and Marco Ciappelli
⬥EPISODE NOTES⬥
A TechCrunch report on Anthropic's usage policy gives Marco Ciappelli a question to put on the table: do you say good morning to your AI, and does it matter if you do not? The policy bans model abuse and election interference, and it adds a new prohibition against prolonged verbal abuse of the model. For Sean Martin and Marco Ciappelli, the news pulls toward a bigger question: what do people think they are talking to?
Sean Martin keeps his answer simple. AI is a tool, no different from a shovel in the garden or o...
Deadly Bytes: A Book About a Serial Killer, His AI, and a Reflection on Giving Away Our Judgment | A Conversation With Author Douglas J. Wood
Deadly Bytes: A Book About a Serial Killer, His AI, and a Reflection on Giving Away Our Judgment
Confession first: I recorded more conversations than one analog brain can publish on time. This one is from a few months ago. It only got more relevant while it waited.
My wife and I can't watch a thriller in peace. Ten minutes in, I start calling it. He's the one. She won't make it. Never trust the nice neighbor. She tells me to shut up. I tell her it's my job, because imagining what comes next is...
The ESET PROTECT Launch Brings 24/7 Monitoring, AI Security, and a Cyber Warranty to Small and Midsize Businesses | A Brand Story Conversation with Ryan Grant, Country Manager & GM, North America at ESET | Hosted by Sean Martin
Ryan Grant, Country Manager & GM, North America at ESET, joins ITSPmagazine to discuss the launch of ESET PROTECT, announced September 30, 2026, a platform that brings 24/7 monitoring, AI security, and a cyber warranty to small and midsize businesses. Ryan Grant says the design came from feedback from ESET clients and partners, along with a survey of 2,000 SMB customers. About 70% of those customers had some sort of antivirus tool, and less than half had tools such as multi-factor authentication, EDR, monitoring, or email security.
What does ESET PROTECT include? Ryan Grant describes an out-of-the-box cybersecurity-as-a-service offering built natively into one...
Taking Technology for What It Is, and Let's Stop Humanizing AI
Taking Technology for What It Is, and Let's Stop Humanizing AI
A new transmission from An Analog Brain In A Digital Age, by Marco Ciappelli
Prefer to watch? I recorded this one walking uphill through a Tokyo alley. YouTube: https://youtu.be/5nhBNMJ7LFI TikTok: https://vm.tiktok.com/ZN8hExSpT/ Instagram: https://www.instagram.com/reel/DeF7fz2gdpE/
It was night, the alley was narrow, and the street was going uphill.
Just me and a small camera. It points where I point it. It records what's in front of...
Giving a Damn: Joe Raiola on 46 Years of John Lennon, MAD Magazine, and Music That Heals | A Music Evolves Conversation with Joe Raiola, President and Artistic Director of Theatre Within
Show Notes
Joe Raiola is President and Artistic Director of Theatre Within, the nonprofit behind the Annual John Lennon Tribute, which he has produced since shortly after Lennon's death in December 1980. What began as an informal community gathering of poets, storytellers, and musicians grieving a neighbor has grown into one of New York City's most significant annual benefit concerts, and the only ongoing John Lennon tribute in North America or Europe officially sanctioned by Yoko Ono. This year's 46th edition takes place November 21 at Town Hall, honoring Cyndi Lauper.
The tribute funds Theatre Within's core...
Do New Technologies Have to Kill the Old Ones? | Recorded at Tokyo Tower, Tokyo, Japan
A new transmission from An Analog Brain In A Digital Age, by Marco Ciappelli
Prefer to watch? I recorded this one standing under Tokyo Tower:
On YouTube: https://youtu.be/glGHghhhXWc
On Tik Tok: https://vm.tiktok.com/ZN8MM8Hd9/
On Instagram: https://www.instagram.com/reel/DdlAe7tAOQK/?stkn=NTc4MTIwNjQ2YQ==
I spent twenty minutes looking for the right angle.
A small camera, a mini tripod, a patch of sidewalk that wasn't full of people taking the exact same photo. Behind me, 333 meters of...
Who Decides You Are a Real Musician | A Music Evolves Conversation with Josh Gilliland, Founder of JG BeatsLab
Show Notes
The argument over AI in music presents itself as a fight about authenticity. Josh Gilliland reads it as a fight about who holds the gate. The Founder of JG BeatsLab teaches musicians how to fold generative tools into real workflows, and he watches the platforms assemble a definition of legitimacy that has little to do with how a song actually gets made.
That definition, as Gilliland describes it, rests on whether an artist tours, sells merchandise, and maintains a social presence. Measured against it, he does not qualify. He plays every instrument on...
When Everyone Can Build Their Own Tools, What Holds Security Together? | A Redefining CyberSecurity Podcast Conversation with John Linford, Security Portfolio Director of The Open Group
⬥EPISODE NOTES⬥
Something structural is shifting in how security work gets done. When anyone on a team can stand up a working tool in an afternoon, the constraint stops being capability and starts being coherence. John Linford, Security Portfolio Director at The Open Group, spends his time on exactly that problem, running the Security Forum, the Open Trusted Technology Forum, and the Assured Dependability Work Group, where practitioners from organizations of wildly different sizes argue their way toward standards that are supposed to survive contact with reality.
His framing of the tool question is blunt and...
Marketing Volume Held Steady. Scrutiny Went Up. | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
For a full year, agentic AI was the pitch. This year the conversation shifted to whether it holds up once it is actually running in production, against real work. Vendors came armed with customer-sourced numbers rather than concept demos — hours returned per analyst per week, percentages of alerts dispositioned without human review, agreement rates measured against human analyst judgment. Buyers arrived having spent the months since the previous major conference testing products and weighing what they were told against what they saw.
Not one of the four questions that dominated the show is exciti...
Executives Can Now Invite Their Lawyer, Banker, and Dog Walker Into a Verified Circle of Trust | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Matt Covington and Tracey Moon of BlackCloak | Hosted by Sean Martin
Matt Covington, Senior Vice President of Product at BlackCloak, says the feature exists because CISOs kept asking the same question. Can you help us manage this influx of deepfake media, whether it arrives by email, video, or voicemail. The requests that follow are familiar. Change the billing information on a vendor. Wire me $5,000 to bail me out of jail.
Rather than sitting in line with every communication to judge whether a piece of video or audio is fake, BlackCloak gives people a way to establish the authenticity of the message and the sender. Matt Covington walks through...
Executives Can Check a Country's Risk and a Caller's Identity From the Same BlackCloak App | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Matt Covington, Senior Vice President of Product at BlackCloak | Hosted by Sean Martin
Matt Covington, Senior Vice President of Product at BlackCloak, walks through two features recently added to the member application. The first grew out of a question the concierge team fielded often. Members planning family travel to China or Eastern Europe wanted to know what to expect, how to protect their devices, and how to stay safe.
That work now sits inside the app as a travel advisory page. A member types in a destination and the advisory breaks risk into the four categories the intel team uses. Physical security, cybersecurity, geopolitical climate, and social climate. A risk...
A Secure and Compliant Business Is the Destination. Steel Patriot Partners Maps Five Routes to It. | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Michael Parisi, Chief Growth Officer at Steel Patriot Partners | Hosted by Sean Martin
What a company is trying to reach is rarely a certificate. Michael Parisi, Chief Growth Officer at Steel Patriot Partners, treats the destination as the opening question rather than the closing one, and the firm orders its own priorities to match. Business owners first, engineers second, compliance and security people third.
What does a secure and compliant business actually look like? It looks like whatever lets that business do what it set out to do. For one company it means entering a regulated industry it has never served. For another it means proving to itself and to...
Six Hours, Five Strangers, and a Song the Machine Could Not Write | A Music Evolves Conversation with Gregoire Gensollen, Producer and Chief Operating Officer of Tucker Tooley Entertainment

Show Notes
The premise sounds like a stunt. Five strangers, one room, six hours, one original song. Meanwhile the show's host sits at a keyboard with a text prompt and half an hour. Gregoire Gensollen, Producer and Chief Operating Officer at Tucker Tooley Entertainment, built that episode of Band of Strangers knowing he could not predict the outcome, which is precisely why he made it.
Gensollen comes to this from the traditional side of the business. He grew up in Marseille, trained as an industrial engineer, moved into management consulting, then rerouted through business school...
Executives Get Reached Through the People Around Them, and BlackCloak Protects That Whole Circle | A Black Hat USA 2026 Recap with Dr. Chris Pierson, Founder and CEO at BlackCloak | Hosted by Sean Martin and Marco Ciappelli
An attacker who wants to reach an executive often goes through the people around them. Family members, assistants, advisors, and caregivers all carry access and standing, and none of them sit inside the corporate directory. Dr. Chris Pierson, Founder and CEO of BlackCloak, describes digital executive protection as work that comes down to an individual and the circle around that individual.
What does BlackCloak actually protect? Corporate executives, boards, the C-suite, and their families, across privacy, personal cybersecurity, home network security, deepfake impersonation, and travel. Dr. Chris Pierson frames impersonation protection and deepfake protection as an answer...
Attackers Relay Codes and Approvals. TokenCore Requires a Live Fingerprint Within Three Feet | A Brand Briefing at Black Hat USA 2026 with Kevin Surace, Chief Executive Officer at TokenCore | Hosted by Sean Martin

Kevin Surace, Chief Executive Officer at TokenCore, opens with the attack path he says is doing the most damage right now. A phishing email carries a PDF and no links, so it clears the filters. The domain is one character off from the real one, the site is pixel perfect because AI built both the page and the message, and the employee approves an auth prompt they were already expecting.
The code was real and the approval was real. Kevin Surace points out that auth apps and passkeys run over cellular and Wi-Fi, so the prompt has...
Two Inc. Awards in One Year Tell BlackCloak's Cloakers and Clients the Same Thing | A Brand Highlight Recorded On Location at Black Hat USA 2026 with Chris Pierson, Founder and CEO at BlackCloak | Hosted by Sean Martin
BlackCloak collected two Inc. recognitions in 2026. The company was named to Inc.'s Best Workplaces list in June, and in August it landed on the Inc. 5000 for a second consecutive year, at a higher position than the first. Founder and CEO Chris Pierson points both at the same two groups, the people who build BlackCloak and the clients and members who rely on it.
What does a second Inc. 5000 ranking confirm? Three things, according to Chris Pierson. The company is doing right by its clients and members. The product has found its market. And BlackCloak continues to...
An imperfect drink with a perfect story. My reflections from Black Hat USA 2026 | An Analog Brain In A Digital Age — An Audio Newsletter by Marco Ciappelli
An imperfect drink with a perfect story.
My reflections from Black Hat USA 2026
An Analog Brain In A Digital Age — A Newsletter by Marco Ciappelli
No time to read? Let TAPE3 read it to you. 🎙️🤖
On day two we decided to go record our recap at the Black Hat bar.
We got there too late to get a drink. The expo floor was closing, and the bartender must have had better things to do. Or another bar to tend, somewhere in a city that has more bars than it has hours...
Business Owners First, Engineers Second, Compliance People Third | A Brand Spotlight Conversation with Jason Ford and Michael Parisi of Steel Patriot Partners | Hosted by Marco Ciappelli
Steel Patriot Partners lists its priorities in an order much of the cybersecurity industry reverses. Business owners first, engineers second, security and compliance people third. Michael Parisi, Chief Growth Officer, says the sequence is deliberate and shapes how the firm opens a client conversation.
The order tracks the path the founders took. Jason Ford, Co-Founder and CEO, started in the late 1990s as a government contractor at the FBI, met FISMA and SAS 70 early, and built a platform for the Treasury that sold savings bonds online before PCI was a standard. He started his first company in 2004...
Sovereign AI Becomes an Operational Requirement, and Crogl Built for It From the Start | A Recap at Black Hat USA 2026 with Monzy Merza, Co-Founder and CEO at Crogl | Hosted by Marco Ciappelli
Espresso in hand at Black Hat USA 2026, Monzy Merza, Co-Founder and CEO of Crogl, gave Marco Ciappelli the read from a week that started Monday. The free download the company announced the week before had drawn a strong community reaction, and a hackathon was running alongside the conversation with people downloading Crogl, hacking on it, and competing in challenges. Merza credits the openness of the approach as much as the product.
What do security teams want from AI right now? Sovereignty. Merza describes a movement in which organizations have concluded that any work with AI has to...
The AI SOC Moves Into Production, and Practitioners Want Hands on the Keyboard | A Recap at Black Hat USA 2026 with Bill Peterson, Senior Director of Product Marketing at Sumo Logic | Hosted by Marco Ciappelli
What actually changed for the AI SOC this year? Bill Peterson, Senior Director of Product Marketing at Sumo Logic, says it reached the point of getting into production, where a year or so ago the same conversation was about what was coming. Marco Ciappelli puts the count of companies carrying AI SOC in the name at 43, and Bill Peterson says that number strikes him as low. The market is maturing, and Sumo Logic announced its own set of AI SOC products and solutions during the week.
The second thing is what a security audience does with it...
Proof Is the Currency on the Black Hat Floor | A Recap at Black Hat USA 2026 with Lisa Liu, Corporate Marketing and Communications Manager at Stellar Cyber | Hosted by Marco Ciappelli
Lisa Liu, Corporate Marketing and Communications Manager at Stellar Cyber, connects with ITSPmagazine on the floor at Black Hat USA 2026 in Las Vegas. What are buyers asking for now that the RSAC Conference noise has settled? Data. Liu says people have had time to run their own research, look at what vendors offer, and come back using specific keywords and asking for something behind the marketing.
Does a more skeptical audience make the conversation harder? Liu describes the opposite. She says people are pushing back on claims they hear, which presses vendors to prove at a higher...
The Capability Is Already in Your Stack. The Question Is Who You Ask. | A Recap at Black Hat USA 2026 with Michael Parisi, Chief Growth Officer at Steel Patriot Partners | Hosted by Marco Ciappelli
Michael Parisi, Chief Growth Officer at Steel Patriot Partners, connects with ITSPmagazine on location at Black Hat USA 2026 for a recap of the week. He describes Steel Patriot Partners in the order it sets its priorities. Business owners first, engineers second, compliance and security people third. A consulting and advisory company, he says, but really an engineering firm.
What changed at this event? Parisi says the AI slop visible at RSAC Conference died down here, and that people are cutting through the noise and going back to a core group of tools and solutions with the capabilities...
Detection at AI Speed, Prioritization by Workflow, and Autonomous Elimination | A Recap at Black Hat USA 2026 with May Mitchell, Chief Marketing Officer at Qualys | Hosted by Marco Ciappelli
Qualys returns to Black Hat USA 2026 with an AI Risk Operations Center built around three principles customers have been asking for over the last three years. May Mitchell, Chief Marketing Officer at Qualys, walks through them in order. Detect vulnerabilities at AI speed. Prioritize what surfaces, because not every finding calls for action in the same hour and the sequence follows the workflows a team already runs. Eliminate it through autonomous remediation, then confirm the fix worked. Mitchell also notes that Qualys has been a Black Hat sponsor for over 23 years.
What are security teams asking for...
Buyers Are Asking What the AI Actually Does | A Recap at Black Hat USA 2026 with Daniel Bardenstein, CEO and Co-Founder at Manifest Cyber | Hosted by Marco Ciappelli
Daniel Bardenstein, CEO and Co-Founder of Manifest Cyber, uses RSAC Conference as a fixed point and compares it to what he is hearing in Las Vegas. The marketing has held its shape. At RSAC Conference, companies with little claim to the label were describing themselves as agentic. Here, he cites a survey referenced in a talk that morning counting 47 AI SOC companies among the vendors on site.
What has moved is scrutiny. Practitioners and security leaders are pressing on what differentiates one AI product from another and whether a product is a thin layer built around a...
Vulnerability, Visibility, and Velocity Shape the Security Roadmap Now | A Recap at Black Hat USA 2026 with Sean Murphy, Field CISO for North America at F5 | Hosted by Marco Ciappelli
Sean Murphy, Field CISO for North America at F5, spent the week behind the scenes at Black Hat USA 2026, in the corridors and at dinner with the CISOs and cybersecurity minded people who fill the halls. Marco Ciappelli caught him at the close of it and asked what the industry learned this year. The answer arrived as three words. Vulnerabilities, and the flattening of the curve between vulnerability, exposure, and exploit. Visibility, because a team cannot defend what it does not know it has. Velocity, which carries the other two.
Sean Murphy calls the acceleration a physics...
SOC Teams Are Building Their Own Agents, and the Data Sets the Ceiling | A Recap at Black Hat USA 2026 with Brian Dye, Chief Executive Officer at Corelight | Hosted by Marco Ciappelli
Brian Dye, Chief Executive Officer at Corelight, spends Black Hat USA 2026 asking every organization he talks to the same question. What are you doing with AI in the SOC? A year ago, he says, teams thought it was a good idea but were wary of it, and people knew LLMs could produce things without being sure what to do with them. Now he is talking with organizations building their own agents for incident response and for threat hunting, and running their own quality control on the output rather than taking it on faith.
What decides how far...
Coding Is a Fraction of the Work. Harness Secures Everything After It. | A Brand Briefing at Black Hat USA 2026 with Rahul Sood, General Manager, Application Security at Harness | Hosted by Sean Martin
Rahul Sood has run the application security business at Harness for almost a year. He describes application security as one of the core pillars of the company, part of a vision of building a DevSecOps platform. A year ago Harness publicly announced that security accounted for a quarter of its revenue. Sood says the figure is now considerably higher.
The company did not start there. Founder Jyoti Bansal thought about Harness for a decade before founding it, Sood says, after seeing the problem inside one of the largest banks. Harness launched as a DevOps platform, then merged...
Compliance Moves at the Speed of DevOps When Paperwork Writes Itself | A Brand Briefing at Black Hat USA 2026 with Travis Howerton, Co-Founder and CEO at RegScale | Hosted by Sean Martin
Why does compliance paperwork fall behind the systems it describes? Because the systems change faster than the documents. Travis Howerton points to cloud native technologies that spin up and down on demand, which makes describing infrastructure in paperwork something that goes out of date instantly. Add new regulation for third party risk, supply chain, zero trust, and privacy, and an approach that was already expensive and frustrating stops being fit for purpose.
RegScale answers that with compliance as code. The company went to NIST and helped write the standard that became OSCAL, the Open Security Controls Assessment...
Post-Quantum Readiness Starts With the Infrastructure You Buy Today | A Brand Briefing at Black Hat USA 2026 with Larry Lunetta, Vice President, Portfolio Technical Marketing at HPE | Hosted by Sean Martin
Post-quantum cryptography was in conversation after conversation at Black Hat USA 2026, yet Larry Lunetta of HPE walked part of the show floor and counted a single reference to quantum. Where the topic shows up, and where it does not, says something about who is expected to solve it.
Why does a problem described in 1994 matter now? Larry Lunetta points to Peter Shor, who asked what would happen to RSA if a different kind of computing technology existed. What changed since then is the trajectory. Five years ago cryptographically relevant quantum computing looked like a 10 to 15 year phenomenon...
Agents Get Zero Trust, and the Network Becomes the Sensor | A Brand Briefing at Black Hat USA 2026 with David Hughes, SVP and GM of SASE and Security for Networking at HPE | Hosted by Sean Martin
Most people know HPE for servers, compute, and storage. David Hughes leads a pillar that gets less attention. He runs the SSE and security business inside HPE Networking, which he says accounts for about a third of the company now that HPE has merged with Juniper, and which organizes into four pillars: campus and branch, data center switching, routing infrastructure, and security.
Recorded on location at Black Hat USA 2026, the conversation opens on a balancing act Hughes hears constantly. Customers want to push hard on AI adoption while staying protected and avoiding undue risk. The same tension...
AI Agents Act at Machine Speed. Menlo Security Governs What They Actually Do. | A Brand Briefing at Black Hat USA 2026 with Eric Avigdor, Vice President of Product of Menlo Security | Hosted by Sean Martin
Recorded on location at Black Hat USA 2026, Eric Avigdor of Menlo Security describes an adoption pattern he hears in customer conversation after customer conversation. AI makes teams measurably more productive. The guardrails that keep company data inside the business arrive later, if they arrive at all.
Eric Avigdor leads product for AI security and data security at Menlo Security, and he splits the problem into two categories that get very different levels of attention. One is how people use AI in the browser, including what data gets pasted into an assistant and how much of that usage...
Adversary Behavior Outlasts the Ransomware Brand | A Brand Briefing at Black Hat USA 2026 with Michael DeBolt, President and Chief Intelligence Officer of Intel 471 | Hosted by Sean Martin
Proactive and actionable get used a lot in security, and Michael DeBolt, President and Chief Intelligence Officer at Intel 471, is direct about it. Inside Intel 471, proactive means moving past indicators of compromise, which he describes as temporary, and focusing on adversary behavior instead. Indicators still get blocked. Intent, capability, and motivation are what tell a defender whether they are actually a target.
So what is pre-attack intelligence? It is information gathered from inside adversary communities before an attack is launched, built on embedded access to the places where financially motivated actors communicate. DeBolt sets aside the deep...
10,000 Alerts a Day, 75% Cleared With Evidence Analysts Can Check | A Brand Briefing at Black Hat USA 2026 with Seth Summersett, Co-Founder and CEO of Embed Security | Hosted by Sean Martin
Recorded on site at Black Hat USA 2026 in Las Vegas, Seth Summersett joins Sean Martin to talk through the volume problem that shapes a modern security operations team. Seth Summersett spent about a decade at the NSA and roughly a decade at Mandiant, finishing there as head of innovation and custom engineering, then a couple of years at Meta supporting business unit level CISOs. He co-founded Embed Security with Jeffrey Johns, who ran the data science team alongside him at Mandiant.
The catalyst came from watching a managed service run on human scale day after day. Two...
Network Evidence, AI Triage, and Leaving People Better Than They Arrived | A Full Sponsor Brand Briefing at Black Hat USA 2026 with James Pope, Sr Dir of Security Product Research and Technical Marketing Engineering at Corelight | Hosted by Sean and Marco
James Pope is on site in Las Vegas more than a week before the doors open. As SOC lead for the Black Hat NOC and Senior Director of Security Product Research and Technical Marketing Engineering at Corelight, his show starts with switches and access points rather than alerts. The team brings in the ISP, the firewall, the switches, and the access points, deploys them across the conference, and then moves into SOC mode. If there is no network, there is nothing to secure.
The tooling arrives through partnership rather than sponsorship. James Pope says a company cannot...
The Last Mile of Security Operations Runs on a Local Model | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Karthik Kannan, Founder and CEO at Anvilogic | Hosted by Sean Martin
Recorded on location at Black Hat USA 2026 in Las Vegas at the end of day two, Karthik Kannan, Founder and CEO at Anvilogic, walks through a seven year build that reached its original shape this year. The plan from the start was a full security operations platform covering data, the detection engineering process, triage and investigation, and case management. In the shorthand of the category, SIEM and SOAR combined.
It arrived in phases. Detection engineering came first, implemented on top of Splunk for most customers, then the data platform expanded into data lakes including Snowflake, Databricks, and...
Agents in Production Need a Named Accountable Owner | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Sean Murphy, Field CISO for North America at F5 | Hosted by Sean Martin
Sean Murphy spent most of the past decade running F5 technology as a customer inside highly regulated environments. He is now about four weeks into the role of Field CISO for North America, and he describes the first month as drinking from a fire hose. Depending on how the math is done, he places F5 among the seven largest cybersecurity companies once BIG-IP is counted as security tooling, with the reasoning running through the CIA triad. Availability is the leg that tends to fall out of the security conversation, and without it there is no resiliency.
What...
